
FortiManager
FortiManager is a centralized management platform that provides configuration management, policy provisioning, device monitoring, and firmware management for Fortinet network and security devices, available as both an on-premises deployment and a cloud-hosted service.
The FortiManager adapter provides Axonius with visibility into network and security devices managed through Fortinet's centralized management platform, supporting both on-premises and cloud deployments.
Asset Types Fetched
- Devices, Users, Network/Firewall Rules, Alerts/Incidents, Network Routes, Networks, Network Devices
Data Retrieved through the Adapter
The adapter retrieves information to provide visibility into your publicly accessible assets. The retrieved data for each asset type may include:
- Devices - Data such as centralized configuration, policy provisioning, device monitoring, and firmware management for Fortinet devices.
- Users - Information regarding users managed within the Policy & Objects section.
- Network/Firewall Rules - Detailed firewall policy and object data.
- Alerts/Incidents - Log and report information for security monitoring.
Before You Begin
Required Ports
- TCP Port 443
Authentication Methods
- IAM User Credentials - The adapter authenticates using a Username and Password for an API user account created in the Fortinet Identity and Access Management (IAM) portal.
Required Permissions
The adapter connection requires that the IAM user has at least Read-Only access to the following sections in FortiManager:
- Device Manager - To retrieve information on managed devices.
- Policy & Objects - To retrieve user and firewall policy data.
- Log & Report - To retrieve security alerts and incident logs.
- Administrative Domain Read-Only permissions are needed to fetch assets
APIs
Axonius uses the FortiManager API to retrieve asset data.
Axonius sends the following FortiManager JSON-RPC requests. All requests are sent as POST /jsonrpc, and the JSON-RPC method and URL below are in the request body:
Endpoints
exec sys/login/user- Logs in. When Is Hosted On Cloud is enabled, Axonius instead gets a token fromPOST https://customerapiauth.fortinet.com/api/v1/oauth/token/and logs in withPOST p/forticloud_jsonrpc_login/.exec sys/logout- Logs out.get dvmdb/adom- Fetches the administrative domains (ADOMs).get dvmdb/adom/<adom>/device- Fetches the devices of an ADOM.get pm/config/device/<device>/global/system/interface- Fetches the global interfaces of a device (and.../<interface>for each interface).get pm/config/device/<device>/vdom/root/vpn/certificate/local- Fetches the local certificates of a device.get pm/config/device/<device>/vdom/root/system/settings- Fetches the system settings of a device.get pm/config/global/obj/firewall/address- Fetches global firewall addresses. Enabled by Fetch firewall rules.get pm/config/adom/<adom>/obj/firewall/address- Fetches firewall addresses of an ADOM (address6for IPv6 addresses). Enabled by Fetch firewall rules.get pm/config/adom/<adom>/obj/firewall/addrgrp- Fetches address groups of an ADOM. Enabled by Fetch firewall rules.get pm/config/adom/<adom>/obj/firewall/ippool- Fetches IP pools of an ADOM. Enabled by Fetch firewall rules.get pm/config/adom/<adom>/obj/firewall/vip- Fetches virtual IPs of an ADOM. Enabled by Fetch firewall rules.get pm/pkg/adom/<adom>- Fetches the policy packages of an ADOM. Enabled by Fetch firewall rules.get pm/config/adom/<adom>/pkg/<package>/firewall/policy- Fetches the firewall policies of a policy package. Enabled by Fetch firewall rules.get pm/config/adom/<adom>/pkg/<package>/firewall/security-policy- Fetches the security policies of a policy package. Enabled by Fetch firewall rules.get pm/config/adom/<adom>/pkg/<package>/firewall/central-snat-map- Fetches the central SNAT policies of a policy package. Enabled by Fetch firewall rules.get pm/config/adom/<adom>/obj/ips/sensor- Fetches IPS sensors. Enabled by Fetch Threat Profiles.get pm/config/adom/root/_rule/list- Fetches the IPS signature database. Enabled by Fetch Threat Profiles.exec cache/search/where/used/start- Starts a "Where Used" search for a NAT object. Enabled by Fetch "Where Used" References For NAT Objects.exec cache/search/where/used/get/detail- Gets the result of a "Where Used" search. Enabled by Fetch "Where Used" References For NAT Objects.exec sys/proxy/json- Retrieves FortiOS resources (for example policies, addresses, DHCP leases, VPN tunnels, and Wi-Fi data) from the managed FortiGate devices through FortiManager. Enabled by Fetch managed Fortigate devices. SSL VPN users are always fetched this way.get pm/wanprof/adom/<adom>- Fetches the SD-WAN templates of an ADOM. Enabled by Fetch SD-WAN Templates.get pm/config/adom/<adom>/wanprof/<template>/system/sdwan- Fetches the SD-WAN configuration of a template. Enabled by Fetch SD-WAN Templates.get pm/config/adom/<adom>/obj/vpnmgr/vpntable- Fetches the VPN Manager communities of an ADOM. Enabled by Fetch VPN Manager Communities.get pm/config/adom/<adom>/obj/vpnmgr/node- Fetches the VPN Manager community members of an ADOM. Enabled by Fetch VPN Manager Communities.get pm/config/device/<device>/vdom/<vdom>/router/static- Fetches the static routes of a device VDOM. Enabled by Fetch Static Routes.
Generating FortiManager Credentials
- Log in to the Fortinet IAM portal.
- Create a Permission Profile that grants at least Read-Only access to the relevant Administrative Domains (ADOMs) and specific modules.
- Ensure the profile includes access to Device Management, Policy & Objects, and Log & Report.
- Create an IAM API user and assign it to the Permission Profile.
- Record the Username and Password for use in the Axonius connection.
- From FortiManager 7.2 bearer token authentication is supported. If you are using this version follow the instructions in the FortiManager Documentation to create an API Key. Copy the key after you created it.
Supported from Version
This adapter is supported from Axonius version 8.0.12.
Connection Parameters
To connect the adapter in Axonius, provide the following parameters.
Required Parameters
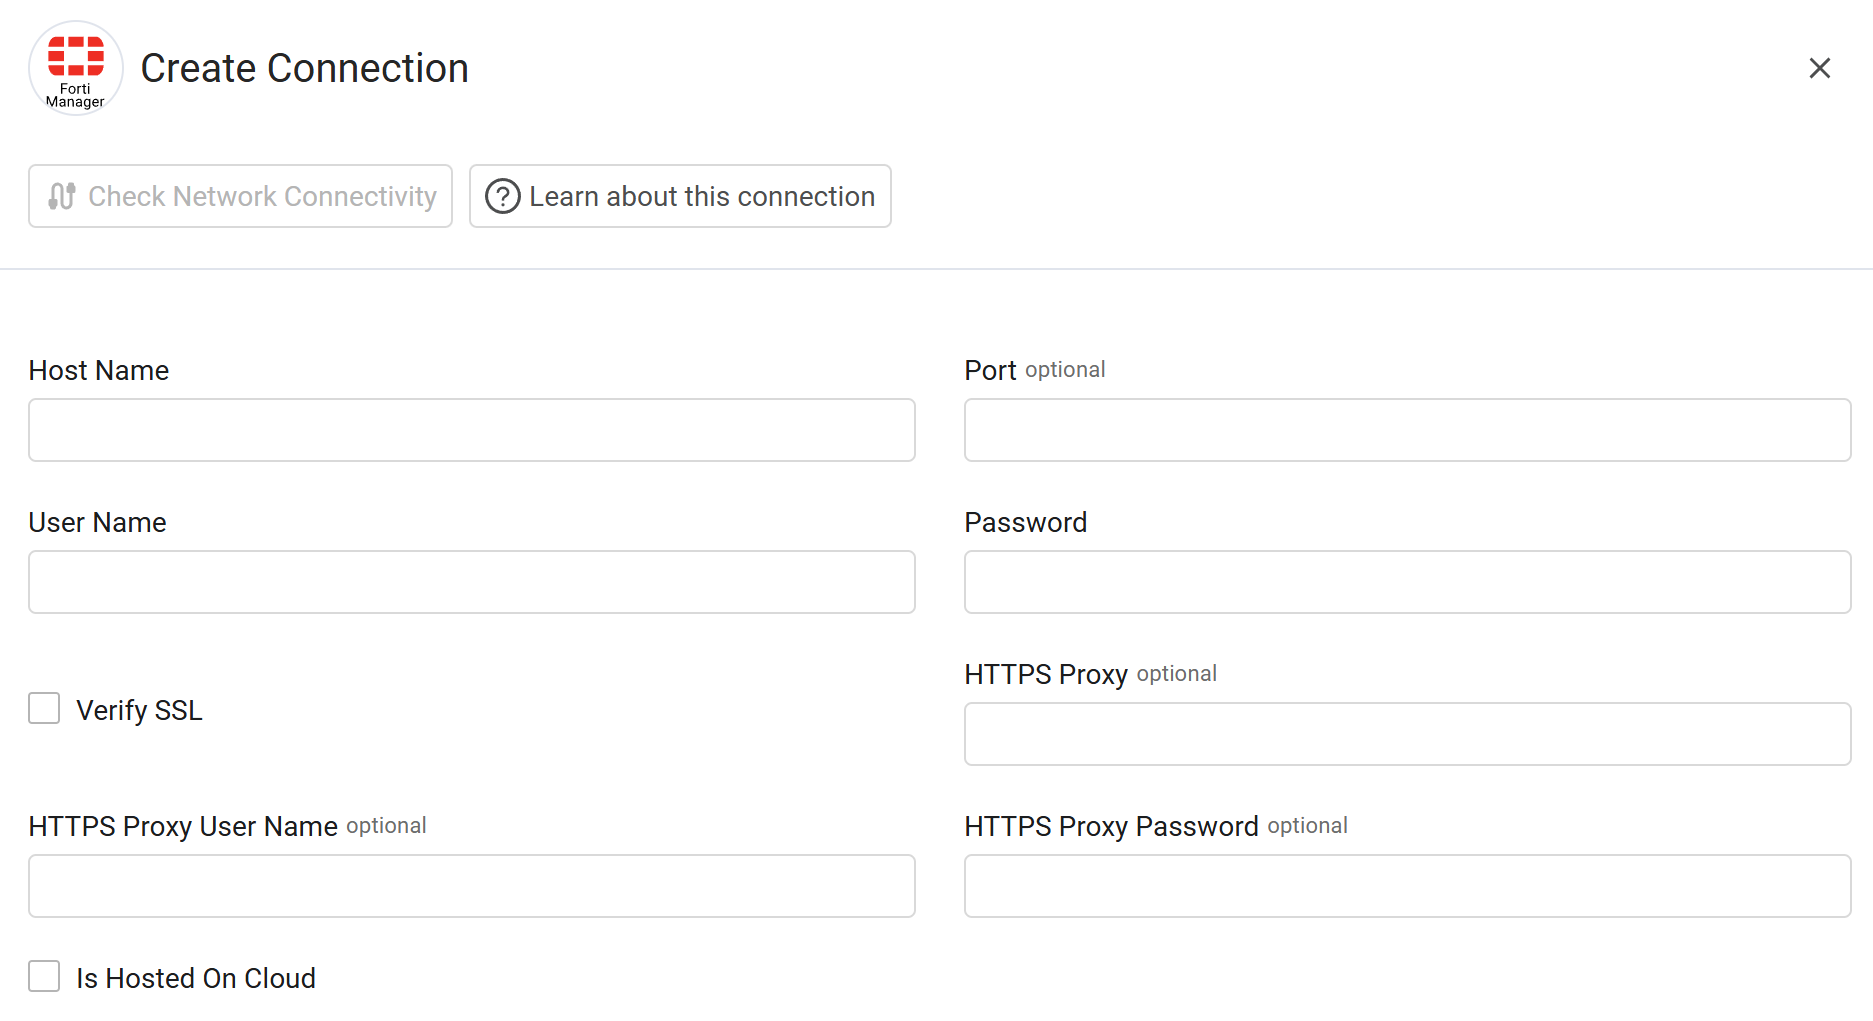
- Host Name - Enter the hostname or IP address of the FortiManager server.
- User Name - Enter the IAM username.
- Password - Enter the password associated with the IAM user.
- API Key - Enter your FortiManager API Key. From FortiManager 7.2 bearer token authentication is supported. If you are using this version of FortiManager, enter an API key.
Optional Parameters
- Port - Enter the specific port for the connection if different from the default.
- Verify SSL - Select whether to verify the SSL certificate of the server against the CA database inside of Axonius. For more details, see SSL Trust & CA Settings.
- HTTPS Proxy - Enter an HTTPS proxy address to connect the adapter to a proxy instead of directly connecting it to the domain.
- HTTPS Proxy User Name - Enter the user name to use when connecting to the value supplied in Host Name or IP Address via the value supplied in HTTPS Proxy.
- HTTPS Proxy Password - Enter the password to use when connecting to the server using the HTTPS Proxy.
- Is Hosted On Cloud - Enable this option if the adapter should connect to FortiManager via FortiCloud hosting.
Advanced Settings
Advanced Settings
Note
- Advanced settings can apply to either all connections of this adapter, or to a specific connection. For more detailed information, see Advanced Configuration for Adapters.
- For more general information about advanced settings, see Adapter Advanced Settings.
- DHCP lease time (seconds) - Enter the duration in seconds for the DHCP lease tracking. By entering a value in this field, you are instructing the adapter to track the validity of the asset's IP assignment for that specific timeframe. If left empty, the adapter relies on its own default internal logic or the data provided directly by the FortiManager API.
- Interfaces exclude list - Enter specific network interfaces to exclude from the fetch.
- Vmware interfaces exclude list - Enter specific VMware network interfaces to exclude.
- Do not fetch OS Type field (default: false) - Enable this to skip fetching the operating system type for devices.
- Allow IPSEC VPN devices (default: false) - Enable this to include IPSEC VPN devices in the fetch.
- Fetch managed Fortigate devices (default: false) - Enable this to retrieve data for FortiGate devices managed by the console.
- Use Fortigate new OS version parser (default: false) - Enable this to use the updated parsing logic for FortiOS versions.
- Fetch firewall rules (default: true) - Enable this to retrieve firewall policy data.
- Maximum number of chunks - Enter the maximum number of data chunks allowed for the fetch (default: 50).
- Fetch VPN SSL Sessions as Devices (default: false) - Enable this to treat SSL VPN sessions as separate device assets.
- Parse Global Interfaces as Network Interfaces (default: false) - Enable this to map global interface data to standard network interface fields.
- Use fetch time for the "Last Seen" field (default: false) - Enable this to set the "Last Seen" timestamp to the current fetch time.
- Fetch Threat Profiles - Select this option to fetch IPS sensor threat profiles and enrich firewall policies with mitigated CVEs
- Fetch "Where Used" References For NAT Objects - Select this option to fetch "Where Used" relationship data for NAT objects. Note that this type of data is quite a heavy fetch, so enable this setting only when needed.
- Allow Empty Hostname For Monitor Devices - Select this option so that monitor devices without a hostname keep their Asset Name empty instead of falling back to the MAC address. Only affects monitor devices.
- Parse IPsec Phase-2 Selectors (default: disabled) - Select this option to add the local and remote subnets of each IPsec tunnel's phase-2 selectors to the tunnel device. Single-host remote selectors are also added as device IP addresses. The adapter uses data that it already fetches. This setting requires Allow IPSEC VPN devices.
- Fetch SD-WAN Templates (default: disabled) - Select this option to fetch the SD-WAN templates of each administration domain (ADOM) and add them to the FortiManager devices that they are assigned to. The data includes zones, members, health checks, and service rules. The adapter sends one request for each ADOM and one for each template.
- Fetch VPN Manager Communities (default: disabled) - Select this option to fetch the VPN Manager communities of each ADOM and add them to the FortiManager devices that are members. The data includes topology, IKE proposals, gateways, and protected subnets. The adapter sends two requests for each ADOM.
- Fetch Static Routes (default: disabled) - Select this option to add the static routes of every device VDOM, read from the FortiManager device database. The adapter sends one request for each device VDOM and does not contact the managed FortiGate devices.
Updated 14 days ago