
Microsoft Endpoint Configuration Manager (MECM)
Microsoft Endpoint Configuration Manager (MECM) (formerly SCCM) is a comprehensive management solution for Microsoft Windows operating systems along with some capabilities for Linux, Mac OS, and mobile devices.
Use cases the adapter solves
MECM is a powerful endpoint management solution that provides a robust inventory of our managed devices in Axonius. Even more importantly, by combining MECM with network/infrastructure data coming from additional adapters, we can identify unmanaged or even rogue devices on the network.
Data retrieved by MECM
Axonius collects common device information such as the hostname, IPs, MAC address, and serial number. The adapter connects directly to the MECM MSSQL database to pull additional device information such as installed software, patches, and collection data.
Types of Assets Fetched
This adapter fetches the following types of assets:
- Devices, Compute Services, Software, SaaS Applications
Before You Begin
Authentication Methods
To connect the adapter, you can use either of the following authentication methods:
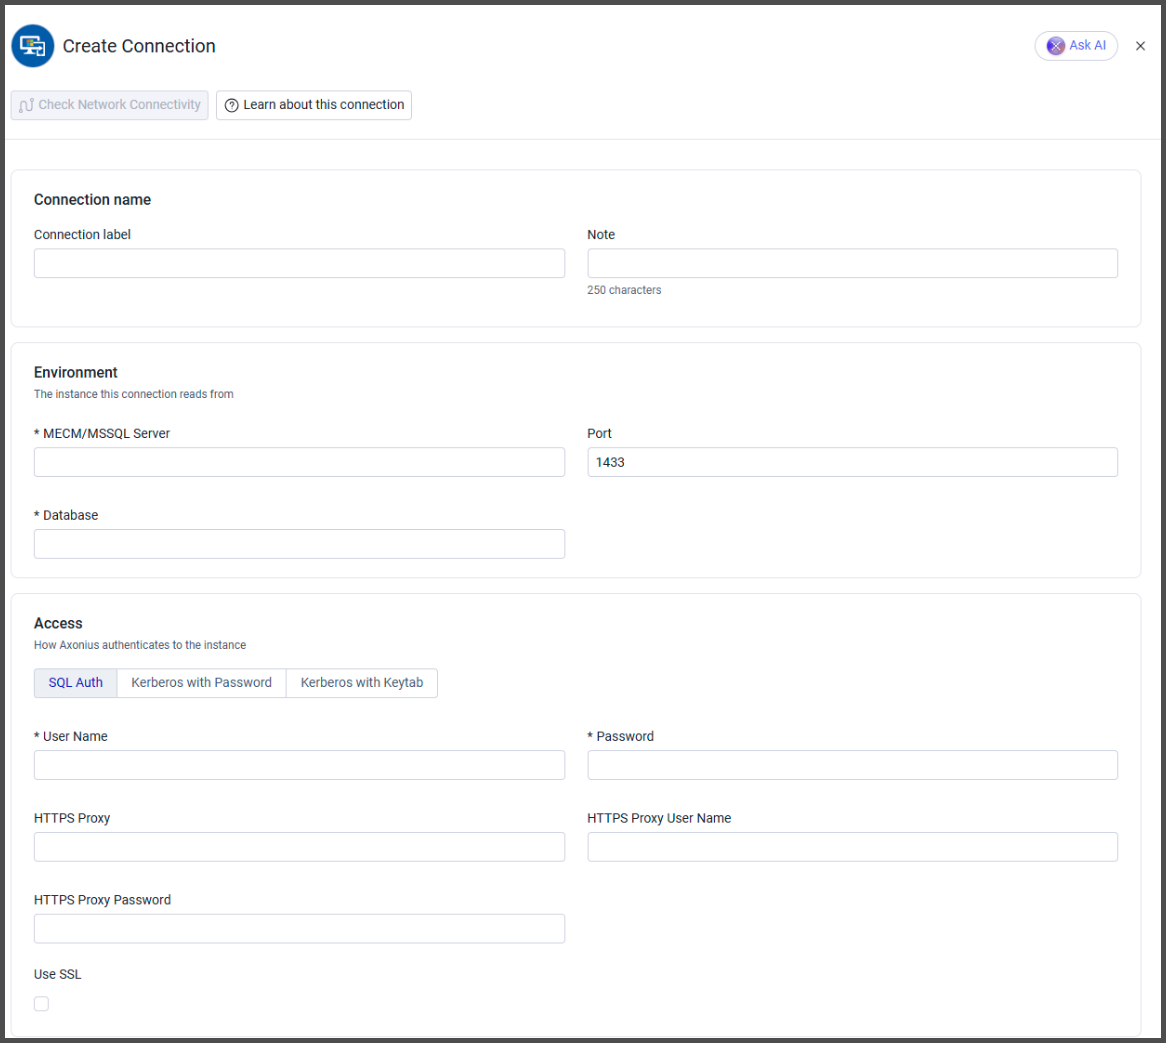
- SQL Auth - Requires a User Name and Password.
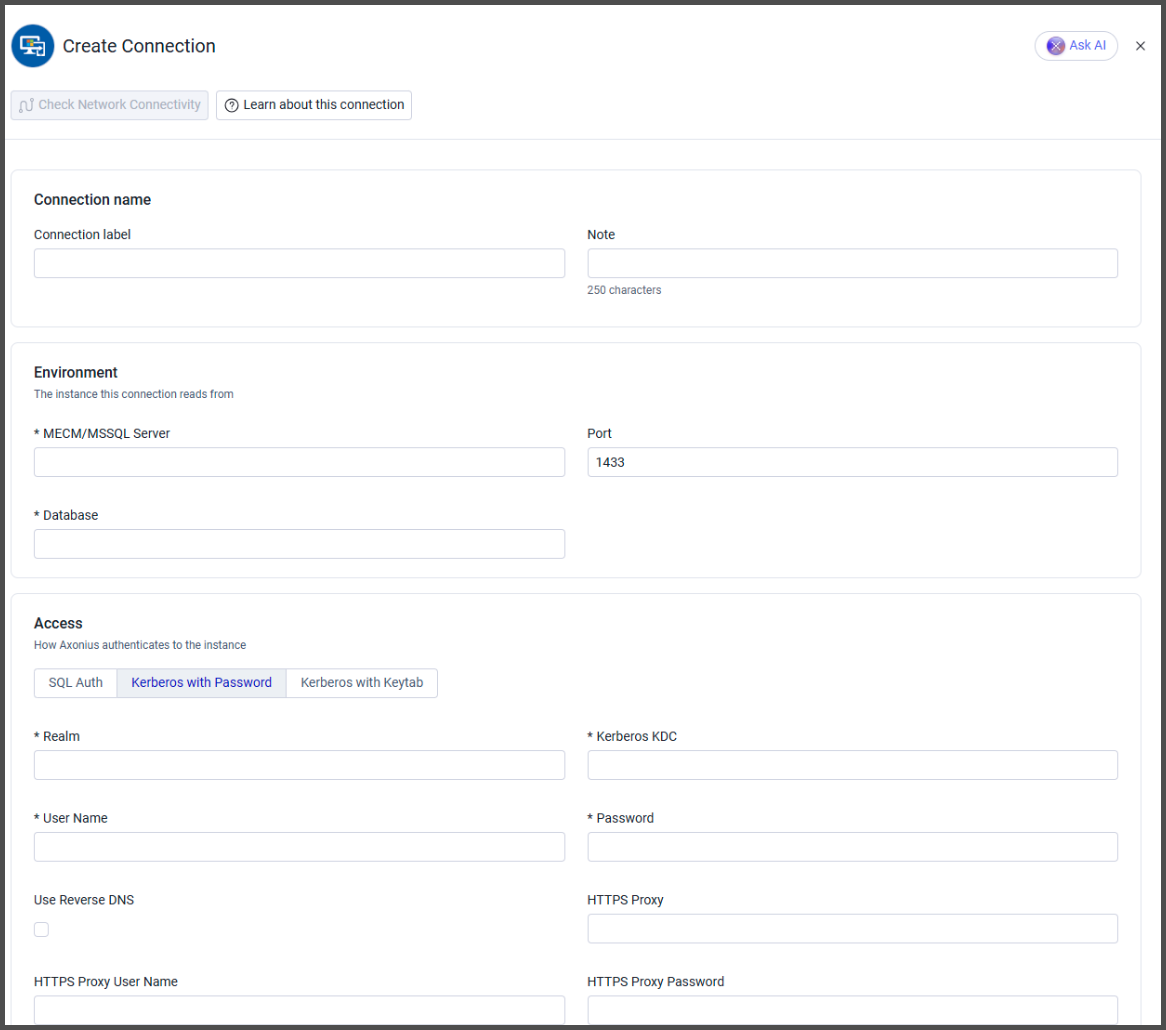
- Kerberos with Password - Requires User Name, Password, Realm, and Kerberos KDC.
- Kerberos with Keytab - Requires User Name, Keytab, Realm, and Kerberos KDC. See Connecting the Adapter in Axonius for more information.
Required Ports
Axonius must be able to communicate with the MSSQL Server via one of the following ports:
- Microsoft SQL Server discovery port - 1433 (default for non SA users) 1434 (default for SA - SuperAdmin - users).
- The specific port for the supplied named instance, if relevant.
- The port appended into the adapter configuration needs to match the global listening port of the SCCM database.
Note
The ports listed above are the standard default SCCM ports. However, these ports might be different if SCCM is deployed and configured with custom ports specified by the customer.
Connecting the Adapter in Axonius
- From the Adapters page, search for MECM and select the adapter.
- Click Add Connection. The Create Connection drawer opens on the Connection Configuration tab.
- Fill in the sections below, then save the connection.
To check that Axonius can reach the source before you enter credentials, click Check Network Connectivity. For more details, see Adding a New Adapter Connection.
Environment
The instance this connection reads from.
- MECM/MSSQL Server (required) - The DNS / IP Address of the Microsoft SQL Server your MECM instance is using.
- To use a specific named instance, the value supplied should be in the following format:
{server_host}\{instance_name}. - If no instance is supplied, the default instance will be used.
- To use a specific named instance, the value supplied should be in the following format:
- Port (default:
1433) - The port used for the connection. The default is 1433. See Required Ports for more information. - Database (required) - The name of the database inside the SQL Server (Usually starts with "CM_").
Access
How Axonius authenticates to the instance. Select one of the authentication methods.
- Authentication Method (required, default: SQL Auth) - Select an authentication method and provide additional parameters accordingly:
-
**User Name** (required) - A user name with read-only permissions .
- The best practice is to create a dedicated SQL local user for Axonius usage. For details, see Creating a Local Read-Only User for Microsoft SQL Server.
- If you are using a domain user, specify the domain and the user name in the following format: domain\username.
-
Password (required) - The user's password. The password must not include ";".
-
HTTPS Proxy - Connect the adapter to a proxy instead of directly connecting it to the domain.
-
HTTPS Proxy User Name - The user name to use when connecting to the value supplied in Host Name or IP Address via the value supplied in HTTPS Proxy.
-
HTTPS Proxy Password - The password to use when connecting to the server using the HTTPS Proxy.
- Realm (required) - The domain in which your Kerberos authentication server has the authority to authenticate users. It needs to be upper case.
- Kerberos KDC (required) - The FQDN for the server or domain controller responsible for the KDC (Kerberos Distribution Center).
- User Name and Password (required) - See SQL Auth. Username needs to be in the format [email protected] (the domain needs to be uppercase)
- Use Reverse DNS (default: disabled) (only when using a Kerberos authentication) - When a Kerberos client connects to a server, it needs to build the SPN (service principal name; for example,
MSSQLSvc/server.domain.com:1433). However, If you only know the IP address of the server, you can try a reverse DNS lookup to resolve the IP back into a hostname. This hostname will then be used in the Kerberos ticket request. If the reverse DNS is misconfigured, Kerberos might generate the wrong SPN, and the authentication will fail.
Note
Generally, you don't need to enable Use Reverse DNS unless you have a network configuration that requires it.
- HTTPS Proxy - Connect the adapter to a proxy instead of directly connecting it to the domain.
- HTTPS Proxy User Name - The user name to use when connecting to the value supplied in Host Name or IP Address via the value supplied in HTTPS Proxy.
- HTTPS Proxy Password - The password to use when connecting to the server using the HTTPS Proxy.
- Realm (required) - The domain in which your Kerberos authentication server has the authority to authenticate users.
- Kerberos KDC (required) - The FQDN for the server or domain controller responsible for the KDC (Kerberos Distribution Center).
- User Name (required) - See See SQL Auth.
- Keytab (required) - Click Upload File to upload a Keytab file.
- Use Reverse DNS (default: disabled) (only when using a Kerberos authentication) - When a Kerberos client connects to a server, it needs to build the SPN (service principal name; for example,
MSSQLSvc/server.domain.com:1433). However, If you only know the IP address of the server, you can try a reverse DNS lookup to resolve the IP back into a hostname. This hostname will then be used in the Kerberos ticket request. If the reverse DNS is misconfigured, Kerberos might generate the wrong SPN, and the authentication will fail.
Note
Generally, you don't need to enable Use Reverse DNS unless you have a network configuration that requires it.
- HTTPS Proxy - Connect the adapter to a proxy instead of directly connecting it to the domain.
- HTTPS Proxy User Name - The user name to use when connecting to the value supplied in Host Name or IP Address via the value supplied in HTTPS Proxy.
- HTTPS Proxy Password - The password to use when connecting to the server using the HTTPS Proxy.
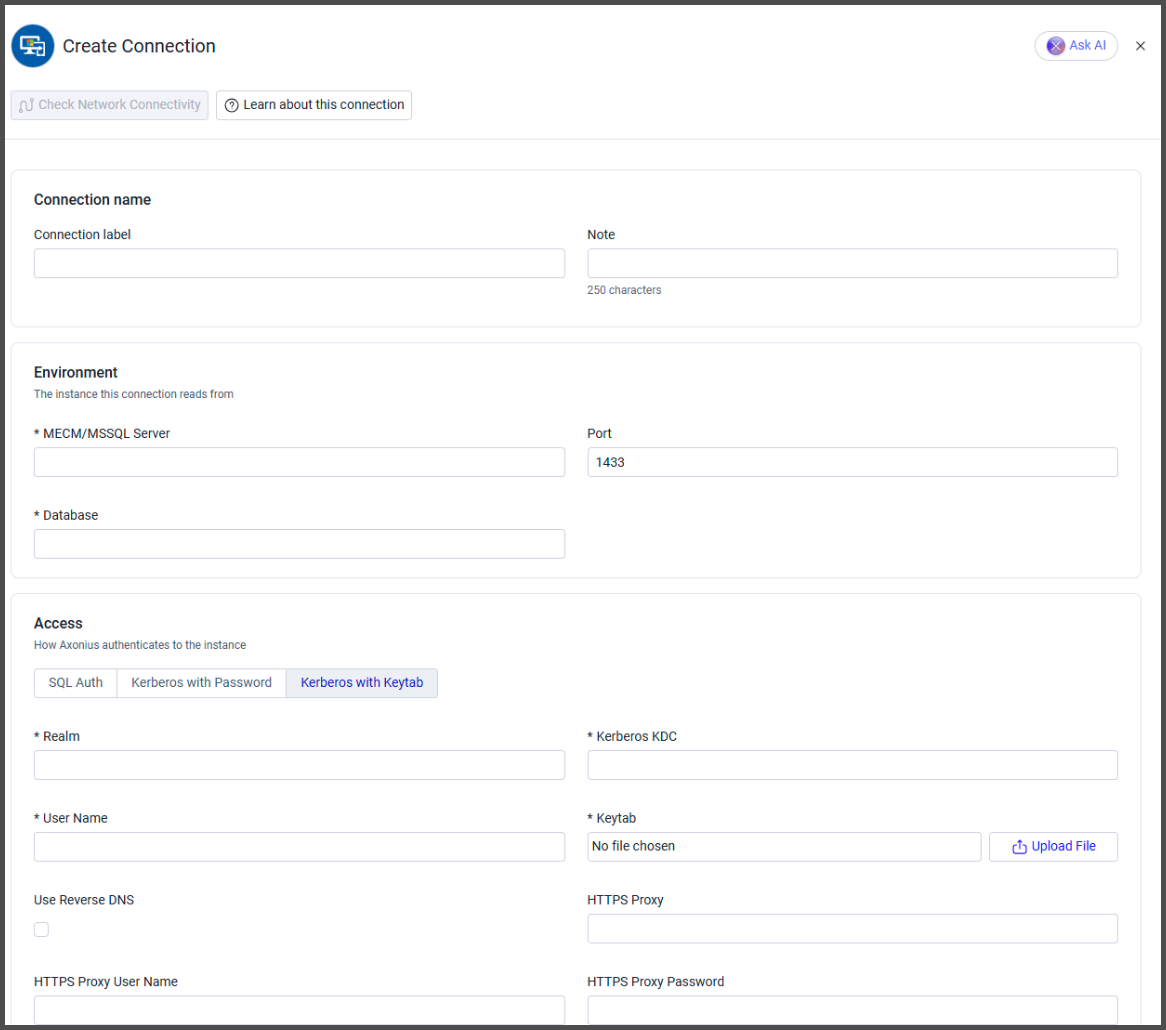
- Use SSL (default: disabled) - Select whether to use SSL.
More Options
- Do not fetch devices without 'Last Seen' (default: disabled) - Select whether to fetch devices without a Last Seen date.
- If enabled, this adapter connection will not fetch devices if they do not have a Last Seen indication.
- If disabled, this adapter connection will fetch devices even if they do not have a Last Seen indication.
- Only include Devices where Client Installed is True - Select whether to only include devices when the ClientInstalled option in MECM is 'True'.
- If enabled, this adapter connection will only fetch devices if they have a ClientInstalled indication.
- If disabled, this adapter connection will fetch devices even if they do not have a ClientInstalled indication.
- Read Only Connection (default: disabled) - Select this option to pass down the parameter “APPLICATIONINTENT=READONLY" to the underlying driver, preventing the connection from modifying any data on the database.
-
Select Gateway – Select the Axonius Gateway to use when connecting adapters whose sources are only accessible by an internal network and not from the primary Axonius instance, which may be an Axonius-hosted (SaaS) instance or Customer-hosted (on-premises / private cloud). To use this option, you need to set up an Axonius Gateway.
To learn more about common adapter connection parameters and buttons, see Adding a New Adapter Connection.
Advanced Settings
Note
Advanced settings can either apply to all connections for this adapter, or to a specific connection. Refer to Advanced Configuration for Adapters.
-
Fetch only active devices (Active0 = 1) - Select to fetch only active devices where the value of Active0 is 1.
-
Exclude IPv6 addresses - Select whether to fetch IPv6 addresses. If cleared, the connections for this adapter will fetch both IPv4 and IPv6 addresses.
-
Device id chunk size - Set the device batch size (Number of devices) that is processed.
-
SQL page size (required, default: 1000) - Set the SQL page size that sent as part of the SQL connection.
-
Machine domain Include list (optional) - Specify a comma-separated list of SCCM domains. If empty, the connections for this adapter will collect devices from any domain.
-
Fetch v_GS_ADD_REMOVE_PROGRAMS software legacy table - Select whether to fetch installed software information from v_GS_ADD_REMOVE_PROGRAMS software legacy table.
-
Fetch files path table (required, default: true) - Select whether to fetch installed software path from the files path table. If cleared, the fetch process for this adapter will be faster.
-
Find software independent files in the system (matching Regex) - Enter a regex expression to search for and fetch files in the device’s software table that usually would not be retrieved because they are ‘independent’ (i.e. executables or other script files not related to any specific software). The data fetched here is displayed in the ‘Software Independent Files’ field. You can only use this option if you enabled ‘Fetch files path table’.
-
Fetch v_GS_INSTALLED_SOFTWARE table (required, default: true) - Select whether to fetch installed software from the v_GS_INSTALLED_SOFTWARE table. If cleared, the fetch process for this adapter will be faster.
-
Fetch DEVICE_INSTALLEDAPPLICATIONS_DATA table - Select whether to fetch installed software from the DEVICE_INSTALLEDAPPLICATIONS_DATA table.
-
Fetch INSTALLED_EXECUTABLE_DATA table - Select whether to fetch installed software from the INSTALLED_EXECUTABLE_DATA table.
-
Fetch vSMS_SUMDeploymentStatusPerAsset table (default: false) - Select this option to fetch data from the 'vSMS_SUMDeploymentStatusPerAsset' table for each asset.
-
Parse all compliance status history per device (required, default: true) - Select whether to parse historical compliance status information to the Current Compliance Status field.
-
Parse the latest compliance status per device (required, default: true) - Select whether to parse the latest compliance status information to the Current Compliance field.
-
Fetch software update compliance with the following statuses - Select up to 4 statuses from the dropdown list: Detection Status Unknown, Not Applicable, Required/Missing, Already Installed/Compliant. The adapter will fetch only the selected statuses.
-
Allowed Collections (optional) - Provide a list of collections to limit the fetch to.
-
Fetch services information (required, default: true) - Select whether to fetch services information for each device. If cleared, the fetch process for this adapter will be faster.
-
Fetch v_GS_SOFTWAREPRODUCT software table (required, default: true) - Select whether to fetch executable files from the v_GS_SOFTWAREPRODUCT table. If cleared, the fetch process for this adapter will be faster.
-
Fetch EP_AntimalwareHealthStatus Windows Defender AV definition table (optional) - Select whether to fetch Windows Defender Health Status from the EP_AntimalwareHealthStatus.
-
Fetch devices from the following additional tables (optional) - Enter a comma- separated list of SQL tables from which additional device information is fetched. If parameter is empty, no additional device information will be fetched for this connection.
-
To be considered a valid table, it should have:
- a column called "ResourceID" or "MachineID" as the device identifier
- less than or equal to 100 columns
- be in the default database (same that has v_GS_COMPUTER_SYSTEM, v_GS_INSTALLED_SOFTWARE, table as e.g.)
-
This feature will fetch all the lines in the table that are associated with devices and add them as a field with the name “Table:
{table_name}” on device-specific information.
-
-
Fetch online data table (required, default: true) - Select whether to fetch fields from the v_CollectionMemberClientBaselineStatus SCCM table. When you select this parameter, Axonius fetches online data from the following fields: CNIsOnline, CNLastOnlineTime, CNLastOfflineTime, CNIsOnInternet, CNAccessMP
-
MSSQL Connection Timeout (required, default: 30) - Specify the number of minutes that elapse before the MSSQL connection times out.
-
Populate "Device:Last Used User" only for users seen within the past X days - Specify the number of past days from which you want the adapter to populate the Last Used User field in the Devices table.
-
Populate Installed Software: Last Used On for software used within the past number of days, greater than 0. (optional, default: 90) -
- When the number entered is greater than 0, the SCCM adapter will fetch results from the Installed Software: Last Used On field in SCCM if the installed software was used within the specified number of days.
- If the field value is zero or empty, Installed Software: Last Used On information won’t be retrieved and the SCCM adapter will have a faster fetch.
-
Custom Admin Data Table Name (optional) - Enter a table name. The table must be in the same database as defined in the adapter connection. This configuration should only be set if the customer is missing Local Admin Data in their SCCM device records. The columns that the user provides are mapped to columns in Axonius and need to be named as shown below in the mapping column.
Axonius field name Name mapped to in Custom Admin Data Table Asset ID ResourceID MachineID Name account0 User0 Account0 Name00 Domain domain0 Domain0 Domain00 SID SID0 User Type Category0 Account00 Account Type Type0 Type00 Status Enabled0 Group name0 LocalSecurityGroup0 Name0 Name00 Last Updated Timestamp TimeKey -
Fetch licenses - Select this option to fetch SCCM licenses.
-
Don't fetch software reported as uninstalled by SCCM (required, default: true) - Select whether to fetch software reported as uninstalled by SCCM.
-
Use "Resource_Domain_OR_Workgr0" as device domain (required, default: false) - By default, the adapter uses the "Full_Domain_Name0" field as the device domain. Select this option to use the "Resource_Domain_OR_Workgr0" field instead.
-
Set asset type by Distinguished Name (default: no rules) - Define rules that fetch MECM device records whose Distinguished Name matches a regular expression as Compute Services instead of Devices. For each rule, enter the Distinguished Name regex (case-insensitive, matches any part of the Distinguished Name), for example
OU=SQL Clusters,, and select the Asset type (Compute Services or Devices). Rules are evaluated in the order entered, and the first match applies. Devices that match no rule are fetched as Devices. To keep an exception as a Device, add a Devices rule above the broader rule. Compute Services are fetched only when at least one rule is configured. -
Last Seen source field (default: Last Active Time) - Select the SCCM client summary field that the adapter uses as the Last Seen value for devices that have an SCCM client installed. Options are Last Active Time (the last time the client was active), Hardware Scan (the last hardware inventory scan), Heartbeat DDR (the last heartbeat discovery record), Status Message (the last status message from the client), and Policy Request (the last policy request from the client). Devices without an SCCM client use the Active Directory logon timestamp. If the selected field has no value for a device, the device has no Last Seen value from SCCM. If Do not fetch devices without 'Last Seen' is selected, such devices are not fetched.
NoteFor details on general advanced settings under the Adapter Configuration tab, see Adapter Advanced Settings.
Troubleshooting
- "Login failed" - If you are using a domain user, in the User Name field, specify the domain and the user name in the following format: domain\username.
Related enforcement actions
Updated 7 days ago