
Cisco Firepower Management Center
Cisco Firepower Management Center provides management over firewalls, application control, intrusion prevention, URL filtering, and advanced malware protection.
Asset Types Fetched
- Devices, Networks, Network/Firewall Rules, Network Routes, Network Devices
APIs
- Axonius uses the Firepower Management Center REST API.
- Review info about Authentication here.
Axonius calls the following endpoints. Endpoints marked with {domainUUID} are called once for each domain available to the user.
Endpoint List
-
POST /api/fmc_platform/v1/auth/generatetoken- Generates the authentication tokens. -
POST /api/fmc_platform/v1/auth/refreshtoken- Refreshes the authentication tokens. -
GET /api/fmc_platform/v1/info/domain- Retrieves the domains available to the user. -
GET /api/fmc_config/v1/domain/{domainUUID}/devices/devicerecords- Retrieves devices. -
GET /api/fmc_config/v1/domain/{domainUUID}/object/hosts- Retrieves host objects. Used when Get the device hosts or Fetch firewall rules is enabled. -
GET /api/fmc_config/v1/domain/{domainUUID}/object/networks- Retrieves network objects. Used when Fetch firewall rules is enabled. -
GET /api/fmc_config/v1/domain/{domainUUID}/object/networkgroups- Retrieves network groups. Used when Fetch firewall rules is enabled. -
GET /api/fmc_config/v1/domain/{domainUUID}/object/interfacegroups- Retrieves interface groups. Used when Fetch firewall rules is enabled. -
GET /api/fmc_config/v1/domain/{domainUUID}/object/securityzones- Retrieves security zones. Used when Fetch firewall rules is enabled. -
GET /api/fmc_config/v1/domain/{domainUUID}/object/protocolportobjects- Retrieves protocol port objects. Used when Fetch firewall rules is enabled. -
GET /api/fmc_config/v1/domain/{domainUUID}/object/portobjectgroups- Retrieves port object groups. Used when Fetch firewall rules is enabled. -
GET /api/fmc_config/v1/domain/{domainUUID}/assignment/policyassignments- Retrieves access policy assignments. Used when Fetch firewall rules is enabled. -
GET /api/fmc_config/v1/domain/{domainUUID}/policy/accesspolicies- Retrieves access policies. Used as a fallback when no policy assignments are returned. -
GET /api/fmc_config/v1/domain/{domainUUID}/policy/accesspolicies/{policyID}/accessrules- Retrieves the access rules of each access policy. -
GET /api/fmc_config/v1/domain/{domainUUID}/policy/accesspolicies/{policyID}/operational/hitcounts- Retrieves rule hit counts. Used when Enrich firewall access rules with hit counts is enabled. -
GET /api/fmc_config/v1/domain/{domainUUID}/policy/ftdnatpolicies- Retrieves NAT policies. Used when Fetch firewall rules is enabled. -
GET /api/fmc_config/v1/domain/{domainUUID}/policy/ftdnatpolicies/{policyID}/natrules- Retrieves the NAT rules of each NAT policy. -
GET /api/fmc_config/v1/domain/{domainUUID}/policy/intrusionpolicies- Retrieves Snort 3 intrusion policies. Used when Enrich firewall access rules with threat profiles is enabled. -
GET /api/fmc_config/v1/domain/{domainUUID}/object/intrusionrules- Retrieves Snort 3 intrusion rules. Used when Enrich firewall access rules with threat profiles is enabled.
Required Permissions
The value supplied in User Name must have the following permissions to fetch assets:
- Devices
>Device Management - Devices
>Certificates - Devices
>QOS - Devices
>Flexconfig Policy - Devices
>Platform Settings - Devices
>VPN - Devices
>Troubleshoot
Permissions for Advanced Settings
The following permissions are required in order to enable the advanced settings:
- Get the device hosts:
- Object Manager
- Fetch firewall rules:
- Object Manager
- Devices
>NAT>NAT List - Policies
>Access Control>Access Control Policy
Parameters
-
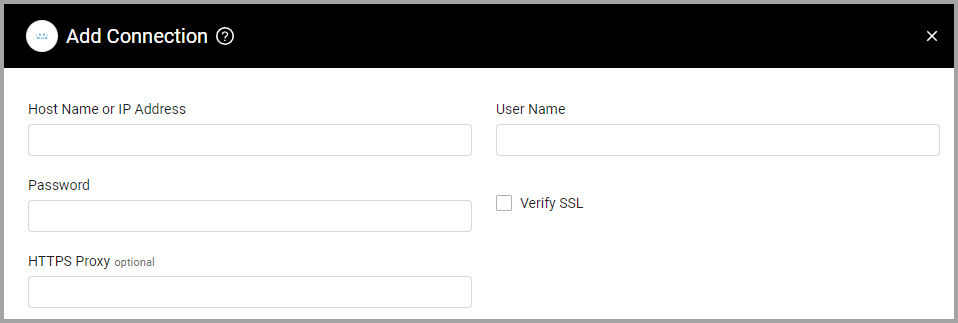
Host Name or IP Address (required) - The hostname or IP address of the Cisco Firepower Management Center server.
-
User Name and Password (required) - The credentials for a user account that has the permissions to fetch assets.
-
Verify SSL - Select whether to verify the SSL certificate of the server against the CA database inside of Axonius. For more details, see SSL Trust & CA Settings.
-
HTTPS Proxy (optional) - Connect the adapter to a proxy instead of directly connecting it to the domain.
To learn more about common adapter connection parameters and buttons, see Adding a New Adapter Connection.
Advanced Settings
Note
Advanced settings can either apply to all connections for this adapter, or to a specific connection. Refer to Advanced Configuration for Adapters.
-
Get the device hosts - Select this option to retrieve all devices of the type host. When enabled, the adapter fetches data from the
object/hostsAPI endpoint, which returns host objects - network objects representing IP addresses or hosts configured in Firepower.Note
You must have the Object Manager permission to enable this setting.
-
Fetch firewall rules - Select this option to fetch firewall rules. For the permissions required to enable this setting, see Required Permissions.
-
Enrich firewall access rules with hit counts - Select this option to enrich firewall rules with hit-counts-per-rule information.
-
Enrich firewall access rules with threat profiles (default: disabled) - Select this option to fetch the Snort 3 intrusion policies and rules, and attach to each firewall access rule the CVEs that its intrusion policy blocks, as a threat profile. This setting requires Fetch firewall rules. Fetching the full intrusion-rule catalog can increase the fetch time.
Note
To learn more about Adapter Configuration tab advanced settings, see Adapter Advanced Settings.
Updated 16 days ago