
Fortinet FortiGate
Fortinet FortiGate is a next-generation firewall providing security and visibility for end-to-end protection across the entire enterprise network.
Note:
For FortiManager use the FortiManager adapter.
Asset Types Fetched
This adapter fetches the following types of assets:
- Devices, Users, Groups, Network/Firewall Rules, Network Devices, Alerts/Incidents, Networks, Network Routes
Before You Begin
APIs
Axonius uses the FortiOS REST API (api/v2) to fetch data directly from a FortiGate. When the connection goes through FortiManager, Axonius uses the FortiManager JSON-RPC API instead. The following endpoints are called:
Endpoints
FortiOS REST API (direct connection):
POST api/v2/authentication- Logs in with a user name and password (DELETE api/v2/authenticationlogs out). Not used with a FortiOS API Key.POST logincheck- Legacy login, used whenapi/v2/authenticationis not available (GET logoutlogs out).GET api/v2/cmdb/system/settings- Fetches the FortiGate system settings.GET api/v2/monitor/system/status- Fetches the hostname, model, version, and serial number.GET api/v2/cmdb/system/vdom- Fetches the list of VDOMs, to build the network topology.GET api/v2/cmdb/system/zone- Fetches the zones of each VDOM, to build the network topology and the intrazone rules.GET api/v2/cmdb/system/interface- Fetches the interfaces, which are fetched as network segments.GET api/v2/cmdb/system/dns- Fetches the DNS servers.GET api/v2/monitor/system/dhcp/- Fetches DHCP leases.GET api/v2/monitor/user/device/select- Fetches user visibility devices.GET api/v2/monitor/user/device/query- Fetches monitor devices.GET api/v2/cmdb/visibility/device-list/- Fetches visibility devices.GET api/v2/monitor/network/arp- Fetches ARP table devices.GET api/v2/monitor/vpn/ipsec- Fetches IPsec VPN tunnels.GET api/v2/monitor/vpn/ssl/- Fetches SSL VPN sessions (as devices when Fetch VPN SSL Sessions as Devices is enabled, and as users).GET api/v2/monitor/wifi/managed_ap/- Fetches managed access points.GET api/v2/monitor/wifi/client- Fetches Wi-Fi clients.GET api/v2/cmdb/switch-controller/managed-switch- Fetches managed switches.GET api/v2/cmdb/wireless-controller/wtp- Fetches wireless access points (FortiAP).GET api/v2/monitor/user/firewall- Fetches firewall users.GET api/v2/cmdb/user/local- Fetches local users.GET api/v2/cmdb/user/group- Fetches user groups.GET api/v2/cmdb/firewall/policy- Fetches firewall policies. Enabled by Fetch firewall rules.GET api/v2/monitor/firewall/policy- Fetches firewall policy statistics. Enabled by Fetch firewall rules.GET api/v2/cmdb/firewall/vip- Fetches virtual IPs. Enabled by Fetch firewall rules.GET api/v2/cmdb/firewall/address- Fetches firewall addresses. Enabled by Fetch firewall rules.GET api/v2/cmdb/firewall/addrgrp- Fetches firewall address groups, including nested groups. Enabled by Fetch firewall rules.GET api/v2/cmdb/firewall.schedule/onetime- Fetches one-time schedules of the firewall policies. Enabled by Fetch firewall rules.GET api/v2/cmdb/firewall.schedule/recurring- Fetches recurring schedules of the firewall policies. Enabled by Fetch firewall rules.GET api/v2/cmdb/firewall/profile-group- Fetches profile groups to resolve the IPS sensor of a policy. Enabled by Fetch firewall rules.GET api/v2/cmdb/ips/sensor- Fetches IPS sensors, when a policy uses one. Enabled by Fetch firewall rules.GET api/v2/cmdb/ips/rule- Fetches the IPS signature catalog, when a policy uses an IPS sensor. Enabled by Fetch firewall rules.GET api/v2/cmdb/system/sdwan- Fetches the SD-WAN configuration. Enabled by Fetch SD-WAN configuration and health checks.GET api/v2/cmdb/system/virtual-wan-link- Fallback forcmdb/system/sdwanon FortiOS 6.x. Enabled by Fetch SD-WAN configuration and health checks.GET api/v2/monitor/virtual-wan/health-check- Fetches the SD-WAN health-check link states. Enabled by Fetch SD-WAN configuration and health checks.GET api/v2/cmdb/vpn.ipsec/phase1-interface- Fetches IPsec phase 1 interfaces. Enabled by Fetch IPsec VPN tunnel configuration.GET api/v2/cmdb/vpn.ipsec/phase2-interface- Fetches IPsec phase 2 interfaces. Enabled by Fetch IPsec VPN tunnel configuration.GET api/v2/cmdb/vpn.ssl/settings- Fetches the SSL-VPN settings. Enabled by Fetch SSL-VPN settings.GET api/v2/cmdb/router/static- Fetches static routes. Enabled by Fetch routing configuration.GET api/v2/monitor/router/bgp/neighbors- Fetches BGP neighbors. Enabled by Fetch routing configuration.GET api/v2/monitor/router/ospf/neighbors- Fetches OSPF neighbors. Enabled by Fetch routing configuration.GET api/v2/cmdb/system.dhcp/server- Fetches DHCP server scopes. Enabled by Fetch DHCP server scopes as Networks.
FortiCloud (when Is Hosted on Cloud is enabled):
POST https://customerapiauth.fortinet.com/api/v1/oauth/token/- Gets an access token.GET https://api.fortigate.forticloud.com/forticloudapi/v1/devices/- Lists the FortiGate devices that are registered in FortiCloud. The FortiOS endpoints above are then called for each device throughforticloudapi/v1/fgt/<serial>/.
FortiManager JSON-RPC API (connection through FortiManager). All requests are sent as POST /jsonrpc, and the JSON-RPC method and URL below are in the request body:
exec sys/login/user- Logs in.exec sys/logout- Logs out.get dvmdb/adom- Fetches the administrative domains (ADOMs).get dvmdb/adom/<adom>/device- Fetches the devices of an ADOM.get pm/config/device/<device>/global/system/interface- Fetches the global interfaces of a device (and.../<interface>for each interface).get pm/config/device/<device>/vdom/root/vpn/certificate/local- Fetches the local certificates of a device.get pm/config/device/<device>/vdom/root/system/settings- Fetches the system settings of a device.get pm/config/global/obj/firewall/address- Fetches global firewall addresses.get pm/config/adom/<adom>/obj/firewall/address- Fetches firewall addresses of an ADOM (address6for IPv6 addresses).get pm/config/adom/<adom>/obj/firewall/addrgrp- Fetches address groups of an ADOM.get pm/config/adom/<adom>/obj/firewall/ippool- Fetches IP pools of an ADOM.get pm/pkg/adom/<adom>- Fetches the policy packages of an ADOM.get pm/config/adom/<adom>/pkg/<package>/firewall/policy- Fetches the firewall policies of a policy package.exec sys/proxy/json- Retrieves FortiOS resources from the managed FortiGate devices through FortiManager (the FortiOScmdbandmonitorendpoints listed above).
Required Permissions
The value supplied for User Name, if used when connecting the adapter, must have read access to devices.
To fetch the network topology, the user must also have read access to the system interfaces, zones, and VDOMs. If the user cannot read them, the adapter does not fetch network segments and continues without an error.
In addition, you need to create an Administrator profile and a FortiManager API locally defined API admin user, and assign the required permissions in the process.
Creating an Administrator Profile
-
On the FortiManager GUI, select System Settings
>Admin Profiles>Create New. -
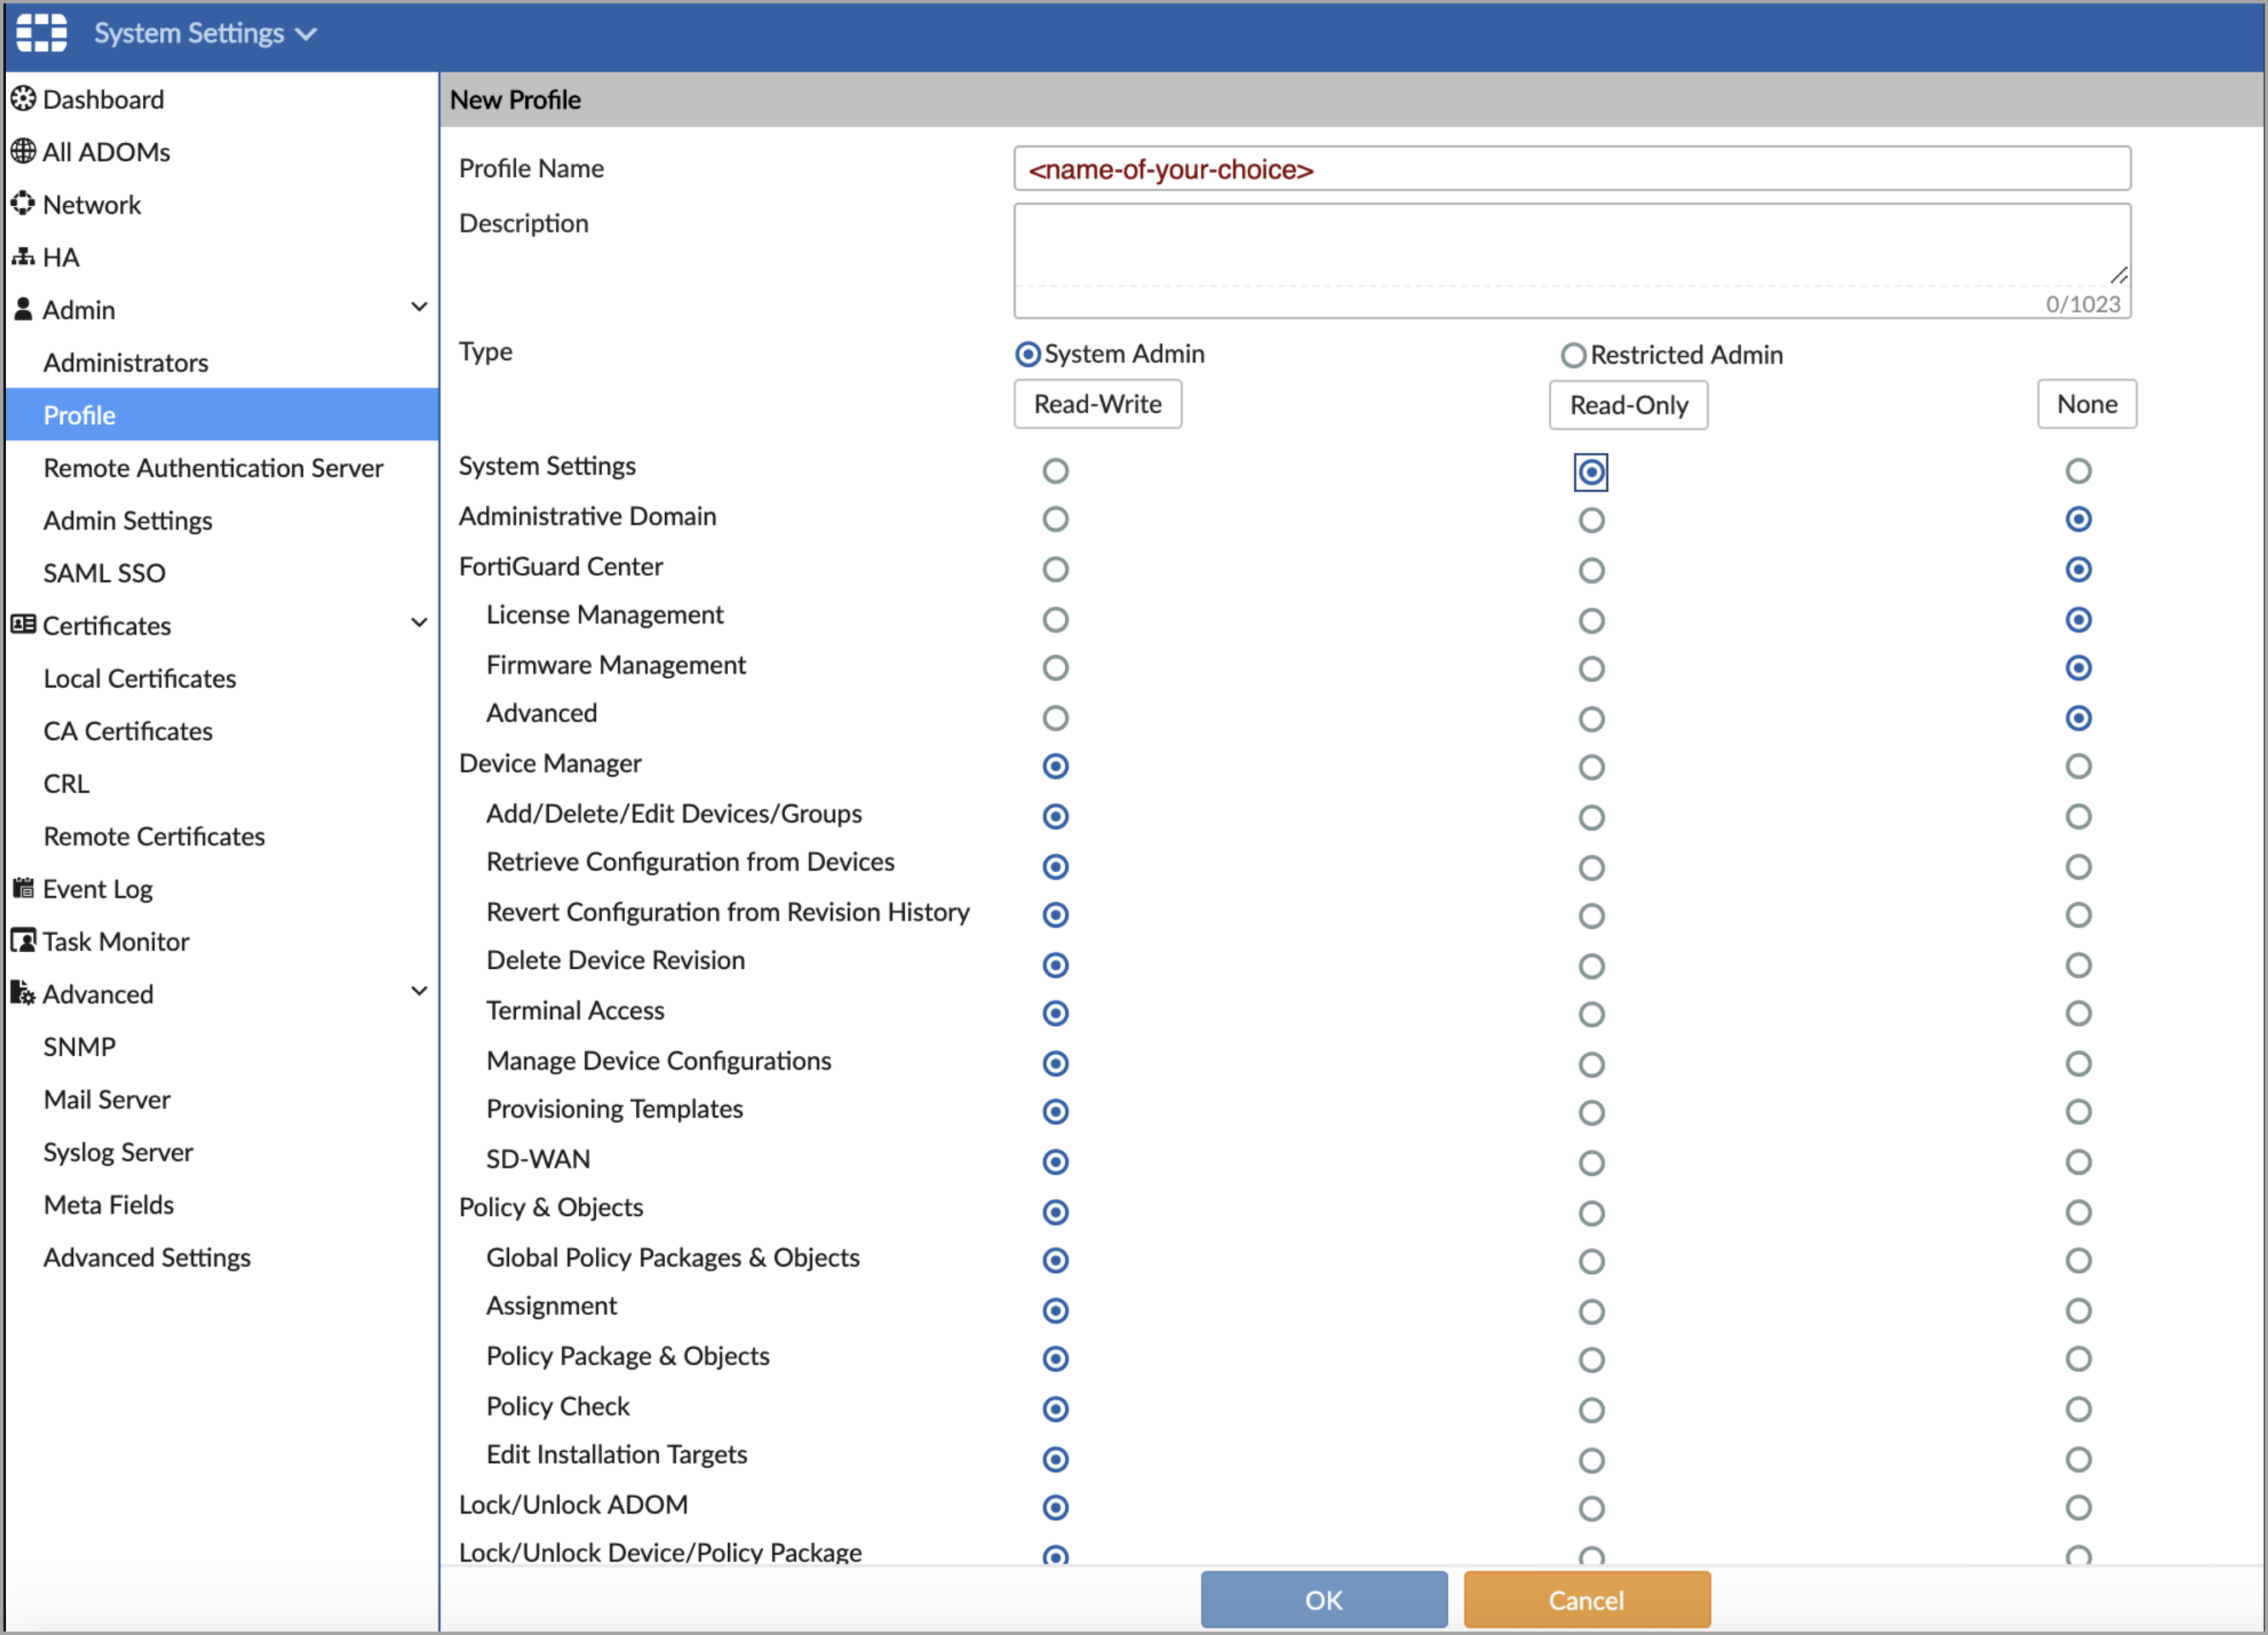
Populate the fields as shown in the image below.
-
Select the permissions of your choice.
-
Click OK.
Creating the JSON API Admin
After you create your administrator profile, use the steps below to create a FortiManager API locally defined API admin user.
Notes
The JSON API admin should have the minimum permissions required to complete the request.
The API admin can be locally defined or defined on some external LDAP, RADIUS, TACACS servers.
-
On the FortiManager GUI, select System Settings
>Administrators>Create New. -
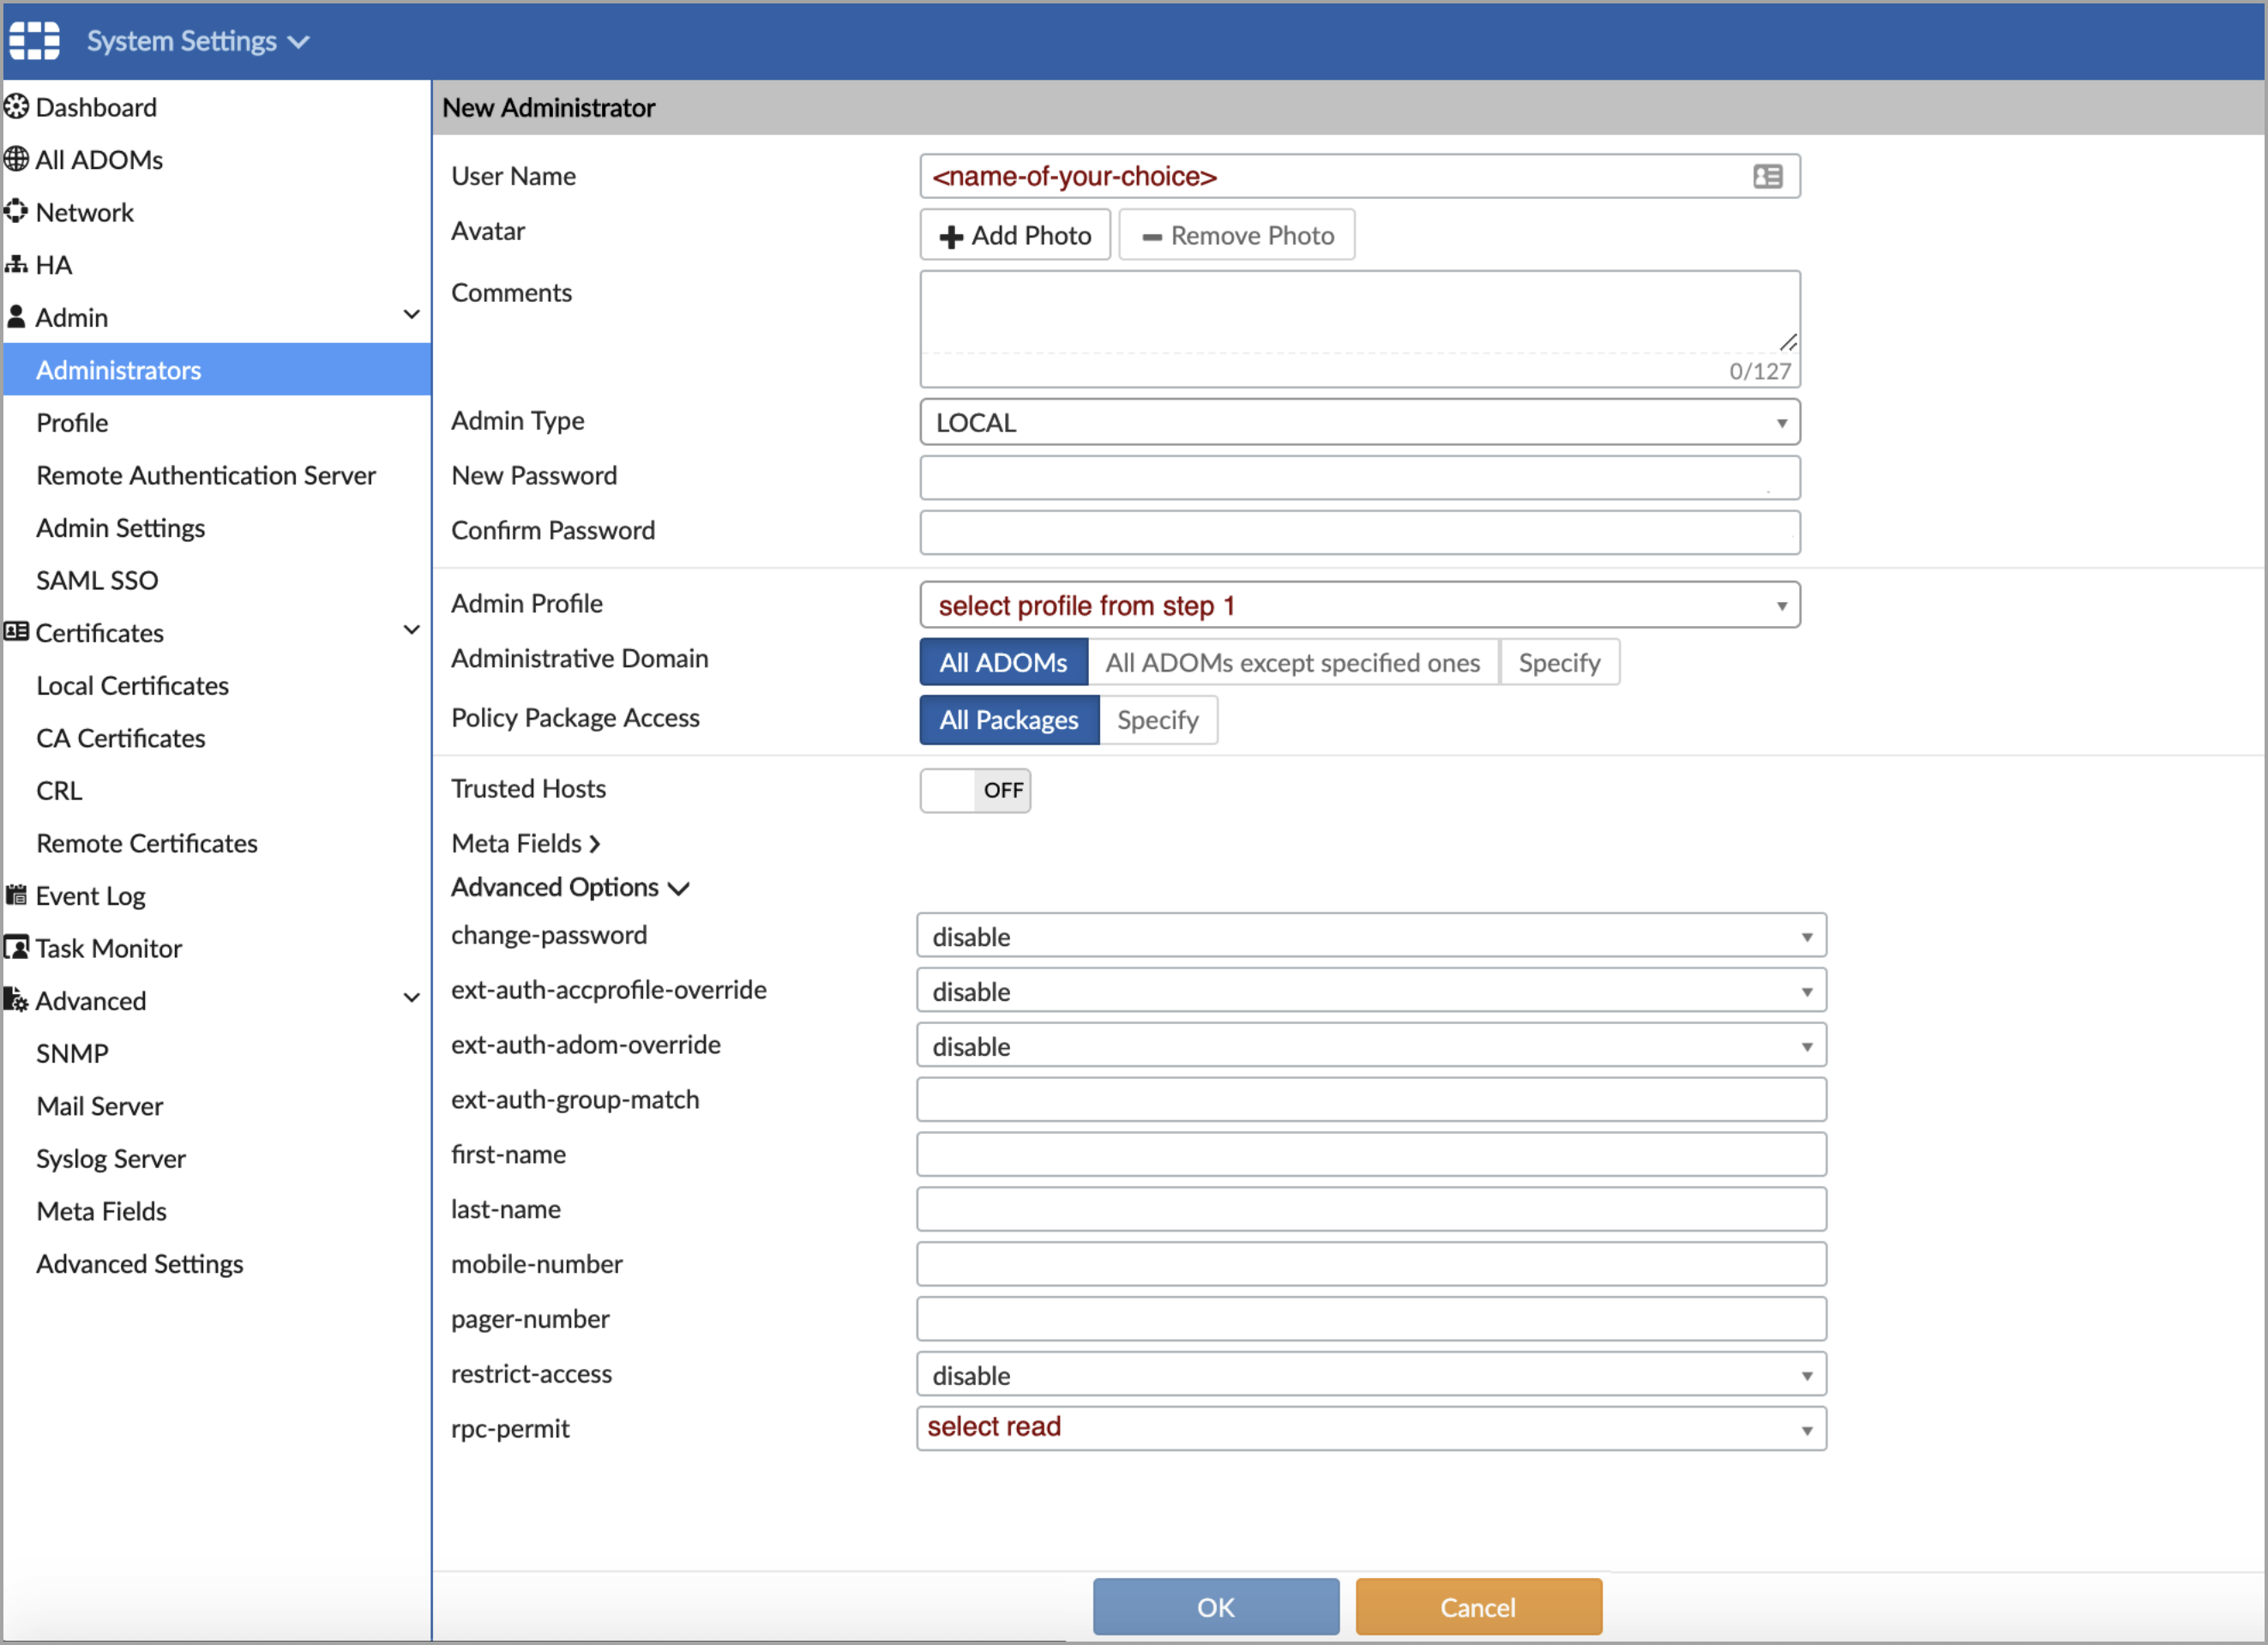
Populate the fields as shown in the image below. Make sure you assign select:read (rpc-permit), ALL ADOMs, and ALL Packages (Policy Package Access).
-
Click OK.
Generating the FortiOS API Key (Optional)
If you authenticate with a FortiOS API Key, you need to create a profile that only has read access to the firewall address permission group.
-
In the FortiGate GUI, select System
>Admin Profiles>Create New. -
Select at least read permissions for:
- User/Device
- Firewall
- Policy
- Address
- Schedule
- Network
- System
- VPN
- WiFi and Switch
-
Click OK.
-
Back in the FortiGate GUI, select System
>Administrators>Create New>REST API Admin. -
Populate the fields as shown below:
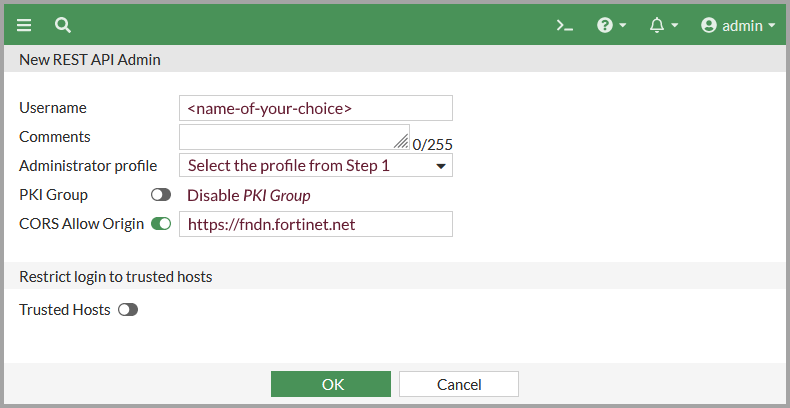
In 6.4.2 and earlier, the Trusted Host must be specified to ensure that your local host can reach the FortiGate. For example, to restrict requests as coming from only 10.20.100.99, enter 10.20.100.99/32.
-
Click OK and an API token will be generated. The API token as it is only shown once and cannot be retrieved. It will be needed for the rest of the process.
-
Click Close.
Deploying the Adapter in Axonius
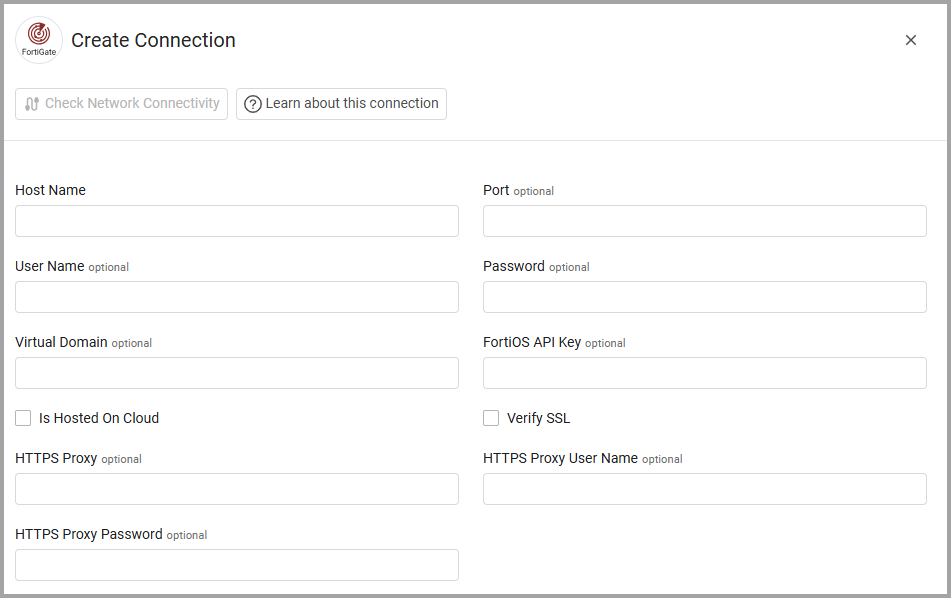
- Host Name - The hostname or IP address of the Fortinet FortiGate server.
- Port - If not supplied, Axonius will use TCP port 443.
- User Name and Password - The credentials for a user account that has the Required Permissions to fetch assets.
-
Note:
As of FortiGate 7.6.6 FortiGate supports only token-based authentication for API calls. Token-based authentication requires the administrator to generate a token, which is then included in each API request for authentication. A token (the FortiOS API Key) is automatically generated when a new API administrator is created in FortiOS.
-
- FortiOS API Key (optional) - An API Key associated with a user account that has the Required Permissions to fetch assets.
Note
For FortiOS connections only:
- User Name and Password are required when FortiOS API Key is not supplied.
- When FortiOS API Key is supplied, User Name and Password are not required, and authentication should be attempted using the Bearer Token.
Optional Parameters
- Virtual Domain - Specify a comma-separated list of Virtual Domains (VDOMs) so that Axonius will fetch data from specified virtual domains. The value applies to all API calls to the FortiGate. When this field is empty, the adapter reads the zones and interfaces of all VDOMs.
- Is Hosted on Cloud - Select this option when Fortinet FortiGate is hosted on Cloud.
- Verify SSL - Select whether to verify the SSL certificate of the server against the CA database inside of Axonius. For more details, see SSL Trust & CA Settings.
- HTTPS Proxy - Connect the adapter to a proxy instead of directly connecting it to the domain.
- HTTPS Proxy User Name - The user name to use when connecting to the value supplied in Host Name or IP Address via the value supplied in HTTPS Proxy.
- HTTPS Proxy Password - The password to use when connecting to the server using the HTTPS Proxy.
To learn more about common adapter connection parameters and buttons, see Adding a New Adapter Connection.
Advanced Settings
Note
Advanced settings can either apply to all connections for this adapter, or to a specific connection. Refer to Advanced Configuration for Adapters.
- DHCP lease time (seconds) (required, default: 604800) - Specify the DHCP lease time, that refers to the life of an IP address remains assigned to a device.
- Interfaces exclude list (optional) - Specify a comma-separated list of Fortinet FortiGate interfaces so that the adapter will only fetch devices that are not associated with the specified interfaces.
- VMware Interfaces exclude list (optional) - Specify a comma-separated list of Fortinet FortiGate interfaces so that the adapter will only fetch virtual devices that are not associated with the specified interfaces.
- Do not fetch OS Type field (optional) - Select to exclude fetching data from the OS Type field.
- Allow IPSEC VPN devices - Select to allow fetching IPSEC VPN devices.
- Use Fortigate new OS version parser - Select this option to fetch the OS minor version from another field on a FortiOS device instance.
- Fetch firewall rules (default: enabled) - Select this option to fetch all the firewall rules, as well as their policies and addresses. When this option is cleared, the adapter does not fetch firewall policies, VIP policies, IPS profiles, addresses, or intrazone rules.
- Maximum number of chunks (default:50) - Enter a number to set the maximum number of parallel chunks to fetch information from the ADOMs. This can be a value between 50 and 100. Select the number of parallel calls that works best with your system.
- Fetch VPN SSL Sessions as Devices - Select this option to fetch VPN SSL sessions as Devices.
- Fetch SD-WAN configuration and health checks (default: disabled) - Select this option to add the SD-WAN zones, members, health checks (with link states), and service rules to the FortiGate device. Available for direct FortiOS connections only. On FortiOS 6.x the adapter reads system/virtual-wan-link.
- Parse IPsec VPN phase 2 selectors (default: disabled) - Select this option to add the local and remote subnets and the status of the IPsec VPN phase 2 selectors to the IPsec VPN tunnel devices. The adapter uses data that it already fetches and sends no additional request. This setting is relevant when Allow IPSEC VPN devices is enabled.
- Fetch IPsec VPN tunnel configuration (default: disabled) - Select this option to add the IPsec phase 1 and phase 2 interface configuration to the IPsec VPN tunnel devices. Available for direct FortiOS connections only. This setting is relevant when Allow IPSEC VPN devices is enabled.
- Fetch SSL-VPN settings (default: disabled) - Select this option to add the SSL-VPN settings (listen interfaces, port, tunnel IP pools, default portal, and authentication rules) to the FortiGate device. Available for direct FortiOS connections only.
- Fetch routing configuration (default: disabled) - Select this option to add the static routes and the BGP and OSPF neighbors to the FortiGate device. Available for direct FortiOS connections only.
- Fetch DHCP server scopes as Networks (default: disabled) - Select this option to create a Network asset (asset type IPv4 Subnet) for each DHCP server scope, with the CIDR blocks, interface, default gateway, DNS servers, DHCP ranges, and reserved addresses. Available for direct FortiOS connections only.
Note
The new requests use the Virtual Domain of the connection. Pre-shared keys and health-check passwords are removed before the data is saved.
Note
For details on general advanced settings under the Adapter Configuration tab, see Adapter Advanced Settings.
Network Topology
Note
Available from Axonius version 10.0.1, for direct FortiOS connections. For FortiManager, use the FortiManager adapter.
The adapter shows the network topology of a FortiGate: its virtual domains (VDOMs), zones, and interfaces. This is the same model used for the Network Topology data of other adapters.
Network Segments
Each FortiGate interface that has an IPv4 address is fetched as a Networks asset with the Asset Type FortiGate Interface Network. An interface with no IPv4 address does not create an asset. The asset includes the following fields:
- Name - The interface name.
- Segment Type - VLAN when the interface has a VLAN ID, otherwise Subnet.
- Network ID - The VLAN ID. Empty for a Subnet.
- Gateway IP - The IP address of the interface.
- Subnets - The subnet of the interface, in CIDR form.
- Is Enabled - Yes when the interface status is up and No when it is down. Empty when FortiOS does not report the status.
- Zone - The zone of the interface. Empty when the interface is not a zone member.
- Interface, Alias, Fortigate Name, and Allow Access - The management access types of the interface.
- Scope Chain - The place of the interface in the FortiGate hierarchy.
Scope Chain
Scope Chain includes the sub-fields Levels and Domain Path. Each level includes Type, Name, Remote ID, Remote ID Source, Order, and Scope ID. The levels, from the outermost level:
- Network Device - The FortiGate. Name is the host name, or the serial number when there is no host name. Remote ID is the serial number and Remote ID Source is Serial.
- Virtual Domain - The VDOM name.
- Zone - The zone name. Only when the interface is a zone member.
- Segment - The interface name.
FortiOS has no IDs for VDOMs, zones, and interfaces, so Remote ID is empty for these levels.
Device Placement
- The FortiGate device includes Scope Chain with one level, Network Device.
- Devices that the FortiGate reports (DHCP leases, ARP entries, and detected devices) include Network Segment Chain under Network Interfaces. The value is the scope chain of the FortiGate interface that reported the device.
Note
A direct FortiOS fetch stops with a connection error when the FortiGate system status has no serial number.
Firewall Rules
Note
Available from Axonius version 10.0.1, for direct FortiOS connections, when Fetch firewall rules is enabled.
Each FortiOS firewall policy is fetched as a Network/Firewall Rules asset with the Asset Type Fortigate Firewall Rule. The asset shows where the policy is enforced, in which order, and which traffic it matches.
Policy Fields
- Priority - The position of the policy in the FortiOS policy list, starting from 1. A lower number is evaluated first.
- Network Security Rules - The rule that the policy enforces:
- Remote ID - The policy UUID.
- Enforcement Point - A scope chain with two levels: Network Device (the FortiGate, by serial number) and Virtual Domain (the VDOM).
- Match Source and Match Destination - One entry for each source or destination interface of the policy. Each entry includes Scope Chain, Allowed Endpoints, and Excluded Endpoints.
- Protocols - ANY when the policy service is ALL. Empty for other services.
Each interface in Match Source and Match Destination is shown as follows:
- A zone, or an interface that is a zone member - The last level of the scope chain is Zone.
- Another interface - The last level is Segment, the same segment as in Network Segments.
- The interface
any- A Segment level namedany.
The source and destination addresses of the policy are shown in Allowed Endpoints. When the policy negates the source or destination address, they are shown in Excluded Endpoints. The adapter also reads address groups, including nested groups. The supported address types are subnet, IP range, and FQDN. The address all means any address.
Some address types, such as country and MAC address objects, are not read. In this case, an allow policy matches only the addresses that the adapter can read, and a deny policy matches all addresses on its interfaces.
Intrazone Rules
Each zone with two or more member interfaces creates an additional rule asset:
- Name - The zone name.
- Rule Type - Intrazone.
- Is Enabled - Yes.
- Action - Allowed when the zone allows intrazone traffic, otherwise Denied (the FortiOS default).
The rule matches the zone to the same zone, for any protocol.
Policies without Network Security Rules
The policy asset is still fetched, but without Network Security Rules, when:
- The policy action is not accept or deny (for example, IPsec).
- The policy uses Internet Service objects.
- The policy also matches on users, user groups, or FSSO groups.
- The policy services are negated.
- The policy has no IPv4 address (IPv6 only).
- A source or destination address resolves to nothing, or an allow policy has a negated side with an address that the adapter cannot read.
Note
Firewall policies from FortiOS connections get a new asset ID that includes the FortiGate serial number and the VDOM. After you upgrade, each policy is shown twice, with the old and the new ID, until the asset cleanup deletes the old asset. Saved queries and enforcements that use the old asset IDs stop matching.
Supported From Version
Supported from Axonius version 4.5
Updated 3 days ago