
Axonius Static Analysis
Axonius Static Analysis identifies Common Vulnerabilities and Exposures (CVEs) within the installed software reported by adapters. To achieve this, Axonius leverages Common Platform Enumerations (CPEs) and the National Vulnerability Database (NVD).
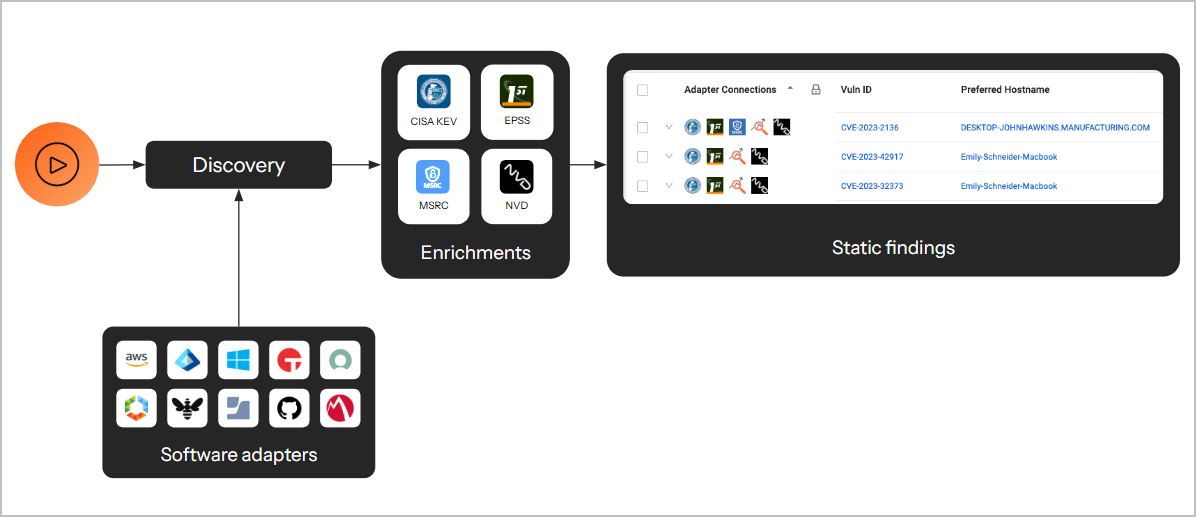
The process includes the following steps:
- Axonius maps every installed software on each device.
- Based on the data extracted from adapter reports, Axonius collects information on each installed software, normalizes and deduplicates the data, to extract the software's name, vendor and version.
- Axonius converts the normalized data into the calculated CPE of the installed software.
- Axonius sends the CPE to NVD to identify all CVEs associated with it.
- Based on the information received from NVD, Axonius lists all CVEs associated with the software installed on each device. Any CVE found in NVD that matches the generated CPE is reported as Static Analysis Findings in Axonius. Such assets have the Axonius Static Analysis icon
 under the Adapter Connection column.
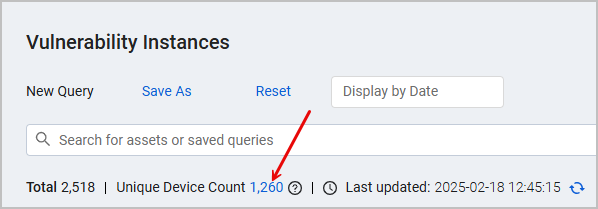
- Security Findings Page assets are created based on the connection made between CVEs and Devices.
Enabling Axonius Static Analysis
To enable Axonius Static Analysis in the system settings:
- Navigate to the System Settings page.
- Select Enrichment and scroll down to Static Analysis Enrichment.
- Enable Fetch software vulnerabilities from NVD DB.
Enriching Vulnerability Data Based on OS
Static Analysis can also fetch CVEs based on data received from operating systems.
Note
Axonius supports fetching vulnerabilities only from operating systems that are supported by the
Figure OSfunctionality - Windows is not supported.
To enable this fetch:
- Navigate to System Settings > Enrichment > Static Analysis Enrichment.
- Enable the following setting (disabled by default): Fetch OS vulnerabilities from NVD DB. (This product uses the NVD API but is not endorsed or certified by the NVD)
The Operating systems supported for this enrichment method are as follows:
- Ubuntu
- Red Hat
- Amazon
- Alma
- Debian
- Fedora
- FreeBSD
- Gentoo
- Arch
- Centos Stream
- Centos
- Rocky
- openSUSE
- SLES
- Cumulus
- iOS
- Oracle Linux
- Oracle Solaris
- IBM AIX
- IBM VIOS
- macOS / OS X
- Arista EOS
- Android
- Cisco
- Fortinet
- VMWare
- PanOS
- Juniper
- HP
- Adtran
Additional Static Analysis Settings
To improve the accuracy of Security Findings generated by static analysis, configure the following, optional settings:
- Exclude CVEs without specific affected versions - Enable this to include only CVEs with an exact software/OS configuration version or a defined version range. When enabled, CVEs whose CPE doesn't identify a specific affected version, or that have a version range with only a start bound and no end bound, are excluded - regardless of whether a version was detected on the asset.
- Exclude CVEs published on or before [date] - Enabe this to set a publication date cutoff to filter out aged CVEs.
- Exclude devices matching this query - Enable this to exclude devices from static analysis based on a selected Devices query. For each device matching this query, static analysis doesn't run against it at all and leaves no CVE fingerprinting.
- Ignore installed software from these adapters - Select adapters where you want the installed software reported by them to not produce static analysis findings.
- The default is empty, so static analysis reads the installed software from all adapters.
- The list shows configured adapters only. For adapters with multiple connections, selecting one connection selects the full adapter.
- To use this setting successfully, you must enable Fetch software vulnerabilities from NVD DB.
- When only Fetch OS vulnerabilities from NVD DB is enabled, the ignore setting is editable but has no affect.
- If both Fetch software vulnerabilities from NVD DB and Fetch OS vulnerabilities from NVD DB are disabled, the ignore setting is greyed out.
- Effect on retrieved data:
- The CVEs reported by the adapters themselves are kept.
- If the same software is reported by a different adapter on the same device, the unignored adapter still produces static analysis findings.
- Installed Software from custom data is still analyzed.
- OS vulnerabilities are not affected.
Updated 20 days ago