---
updatedAt: 2026-09-24T09:48:34.000Z
agentTools:
  projectIndex: https://docs.axonius.com/llms.txt
---

# Microsoft Intune

Microsoft Intune is a management tool that offers mobile device and application management capabilities.

<Callout icon="📘" theme="info">
  Note

  This adapter is in addition to the [Microsoft Entra ID (Azure AD) and Microsoft Intune](/docs/microsoft-azure-active-directory-ad) adapter. Choosing the right configuration depends on your specific data needs. While the [Microsoft Entra ID (Azure AD) and Microsoft Intune](/docs/microsoft-azure-active-directory-ad) combined adapter includes a robust set of advanced settings and enrichments, the Microsoft Intune standalone adapter is more suitable for fetching Intune-specific data, ensuring a cleaner, more modular environment.

  Configuring the combined adapter to fetch Entra ID data only and the standalone adapter to fetch Intune devices is currently the best practice for data separation. If you find that your workflow requires a specific advanced enrichment that is currently unique to the combined adapter, contact Axonius support to add them to the standalone adapter.
</Callout>

### Asset Types Fetched

* Devices, Software, Application Settings, SaaS Applications, Configurations

## Before You Begin

### APIs

Axonius uses the [Microsoft Graph API](https://graph.microsoft.com).

### Permissions

#### General Application Permissions

* DeviceManagementManagedDevices.Read.All - Required to fetch Intune Devices. To set this permission, refer to [instructions for setting permissions on Entra ID, Microsoft 365, and Intune](/docs/microsoft-azure-active-directory-ad#set-permissions).
* DeviceManagementServiceConfiguration.Read.All

#### Permissions for Advanced Settings

See [Advanced Settings](https://docs.axonius.com/docs/microsoftintune#advanced-settings) for the full list.

### Supported From Version

Supported from Axonius version 6.1

## Connecting the Adapter in Axonius

To connect the adapter in Axonius, provide the following parameters:

### Required Parameters

1. **Azure Client ID** - The Application ID of the Axonius application.
2. **Azure Client Secret** - Specify a non-expired key generated from the new client secret.
3. **Azure Tenant ID** - The ID for Microsoft Entra ID.
4. **Cloud Environment** - Select your Microsoft Azure or Microsoft Entra ID cloud environment type.

![IntuneParameters](https://raw.githubusercontent.com/Axonius/ax-docs-pub/refs/heads/main/Images/image-I9WA8OUO.png)

### Optional Parameters

1. **Verify SSL** - Select whether to verify the SSL certificate of the server against the CA database inside of Axonius. For more details, see [SSL Trust & CA Settings](/docs/certificate-settings#ssl-trust-ca-settings).
2. **HTTPS Proxy**   - Connect the adapter to a proxy instead of directly connecting it to the domain.
3. **HTTPS Proxy User Name**  - The user name to use when connecting to the value supplied in **Host Name or IP Address** via the value supplied in **HTTPS Proxy**.
4. **HTTPS Proxy Password**   - The password to use when connecting to the server using the **HTTPS Proxy**.

To learn more about common adapter connection parameters and buttons, see [Adding a New Adapter Connection](/docs/adding-a-new-adapter-connection).

## Advanced Settings

<Callout icon="📘" theme="info">
  Note

  Advanced settings can either apply for all connections for this adapter, or you can set different advanced settings and/or different scheduling for a specific connection, refer to ​[Advanced Configuration for Adapters](/docs/advanced-configuration-for-adapters).
</Callout>

### Global Endpoints Config

* **Fetch Application Settings** - Enable to fetch Application Settings (disabled by default). When enabled, the adapter adds Application Settings assets for settings including device compliance check-in threshold, scheduled actions for noncompliance, device enrollment limit, and Windows Hello for Business configuration. The following API endpoints are called for this fetch:
  * GET /v1.0/deviceManagement
  * GET /v1.0/deviceManagement/deviceEnrollmentConfigurations

### Endpoint Config

This section lists different data types to enrich Devices with. Enable **Fetch Devices from Intune Devices** to be able to select the enrichment data you're interested in.

The following table lists the **Application** permissions required to use each setting.

<Table align={["left","left","left"]}>
  <thead>
    <tr>
      <th>
        Advanced Setting
      </th>

      <th>
        Application Permission
      </th>

      <th>
        Notes
      </th>
    </tr>
  </thead>

  <tbody>
    <tr>
      <td>
        All settings
      </td>

      <td>
        * DeviceManagementManagedDevices.Read.All
        * DeviceManagementApps.Read.All
        * DeviceManagementConfiguration.Read.All
        * DeviceManagementServiceConfig.Read.All
        * DeviceManagementRBAC.Read.All
      </td>

      <td>

      </td>
    </tr>

    <tr>
      <td>
        Fetch Devices from Intune Devices
      </td>

      <td>
        DeviceManagementManagedDevices.Read.All
      </td>

      <td>

      </td>
    </tr>

    <tr>
      <td>
        Enrich Intune Devices with Windows Autopilot Device Identities
      </td>

      <td>
        * DeviceManagementManagedDevices.Read.All
        * DeviceManagementServiceConfig.Read.All
      </td>

      <td>

      </td>
    </tr>

    <tr>
      <td>
        Enrich Intune Devices with Intune Devices Reports
      </td>

      <td>
        * DeviceManagementServiceConfig.Read.All,
        * DeviceManagementConfiguration.Read.All
      </td>

      <td>
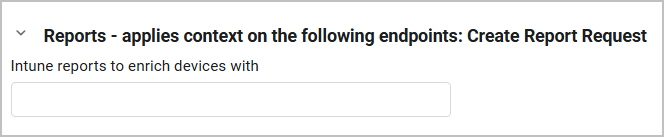
        Expand the bottom **Reports** section to select specific Intune reports to enrich devices with.
        ![](https://files.readme.io/da4a023fb1a0f5efa5712e475b515dd243610b7cbc2b9bf1bc77ae6bee439b24-image.png)
      </td>
    </tr>

    <tr>
      <td>
        Enrich Intune Devices with Discovered Apps
      </td>

      <td>
        * DeviceManagementApps.Read.All
        * DeviceManagementServiceConfig.Read.All
      </td>

      <td>

      </td>
    </tr>

    <tr>
      <td>
        Enrich Intune Devices with Compliance Policy Settings
      </td>

      <td>
        DeviceManagementConfiguration.Read.All
      </td>

      <td>

      </td>
    </tr>

    <tr>
      <td>
        Enrich Intune Devices with Security Baselines
      </td>

      <td>
        DeviceManagementConfiguration.Read.All
      </td>

      <td>

      </td>
    </tr>

    <tr>
      <td>
        Enrich Intune Devices with Specific Fields
      </td>

      <td>
        DeviceManagementManagedDevices.Read.All
      </td>

      <td>
        * Select the fields you want to enrich devices with from the **Fields to fetch** dropdown.
        * **Note for existing connections:** This setting was previously named **Hardware Information**. If you had a connection where this setting was enabled before the name change, the `hardwareInformation` and `physicalMemoryInBytes` fields will be selected to maintain the same data collection behavior. You can change that from the **Fields to fetch** dropdown.
        * This setting increases fetch time substantially. Only enable it if necessary.
      </td>
    </tr>

    <tr>
      <td>
        Enrich Intune Devices with Windows Update Report
      </td>

      <td>
        * DeviceManagementServiceConfig.Read.All
        * DeviceManagementRBAC.Read.All
      </td>

      <td>

      </td>
    </tr>

    <tr>
      <td>
        Enrich Intune Devices with Windows 10 Endpoint Protection Config Statuses
      </td>

      <td>
        DeviceManagementConfiguration.Read.All
      </td>

      <td>

      </td>
    </tr>

    <tr>
      <td>
        Fetch Software from Intune All Apps
      </td>

      <td>
        DeviceManagementApps.Read.All
      </td>

      <td>

      </td>
    </tr>
  </tbody>
</Table>

### Additional Advanced Settings

* **Filter Devices by Ownership Type** - Select which devices to fetch based on their ownership type: all devices, company-owned devices (filters by `managedDeviceOwnerType eq 'company'`), and/or personal/BYOD devices (filters by `managedDeviceOwnerType eq 'personal'`).
* **Fetch Software from Intune All Apps** - Select to fetch all applications registered in Intune. These applications are then saved in Axonius as Software assets and their **Approval Status** is set to Approved. See [Software Registry](/docs/software-approval-list) for more information on approved / unapproved software.

<Callout icon="📘" theme="info">
  Note

  For details on general advanced settings under the **Adapter Configuration** tab, see [Adapter Advanced Settings](/docs/advanced-settings).
</Callout>

## Version Matrix

This adapter was only tested with the versions marked as supported, but may work with other versions. Contact [Axonius Support](mailto:support@axonius.com) if you have a version that is not listed, which is not functioning as expected.

| Version        | Supported | Notes |
| -------------- | --------- | ----- |
| Graph API v1.0 | Yes       | --    |

### Related Enforcement Actions

* [Microsoft Intune - Update Device](/docs/intune-update-device)
* [Microsoft Intune - Delete Managed Device](https://docs.axonius.com/axonius-help-docs/docs/intune-delete-managed-device)
* [Microsoft Intune - Delete Autopilot Device](https://docs.axonius.com/axonius-help-docs/docs/intune-delete-autopilot-device)